




Pragmatic phishing resistantauthentication for government
Overview of use case
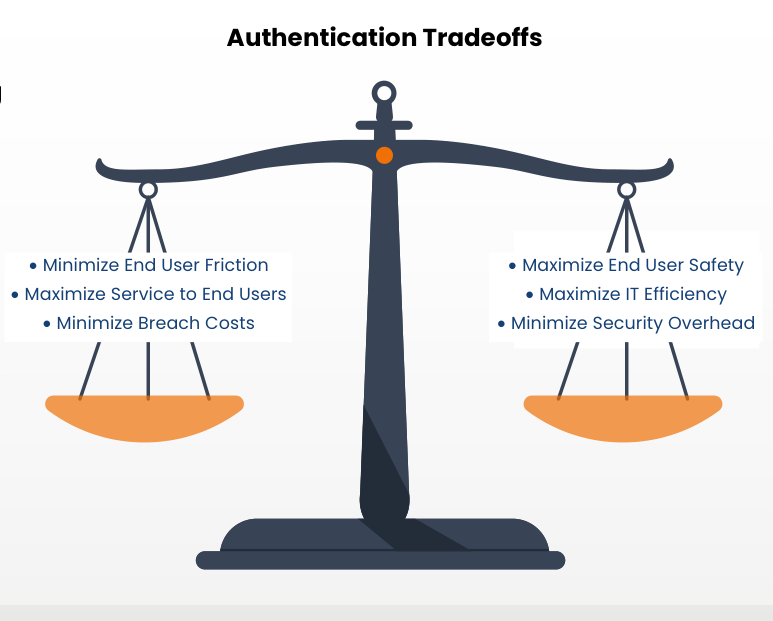
In many important ways, authentication is abalancing act with key tradeoffs:
- End User:Minimum End User Friction is a tradeoff versus End User Safety since increasingsecurity can increase the authentication burden on end users up to the limitwhere pushback occurs.
- IT Resources: Maximize Service to End Userstrades off against IT efficiency since these services can drain scarce ITresources, particularly those that rely on Help Desk support.
- Overheard: Breach and other security downside costsare balanced against overall security budget since “bank vault-level” securitymay not be justifiable for all size of agencies.
Challenges at scale
Asillustrated by the tradeoffs discussed above, phishing resistance challengesare interrelated. So, the challenges are not discrete but instead compound as each challenge isfactored into the full picture:
- Complex environments: Each major component (such as OSand cloud variant) adds complexity.
- UseCase Coverage: No authentication method covers all use cases.
- GroupNeeds: Different groups often require different levels of authentication.
- EndUser Friction: If friction is too high, end users push back.
- ITEfficiencies: Already-constrained IT resources need streamlined utilities tohandle additional demands.
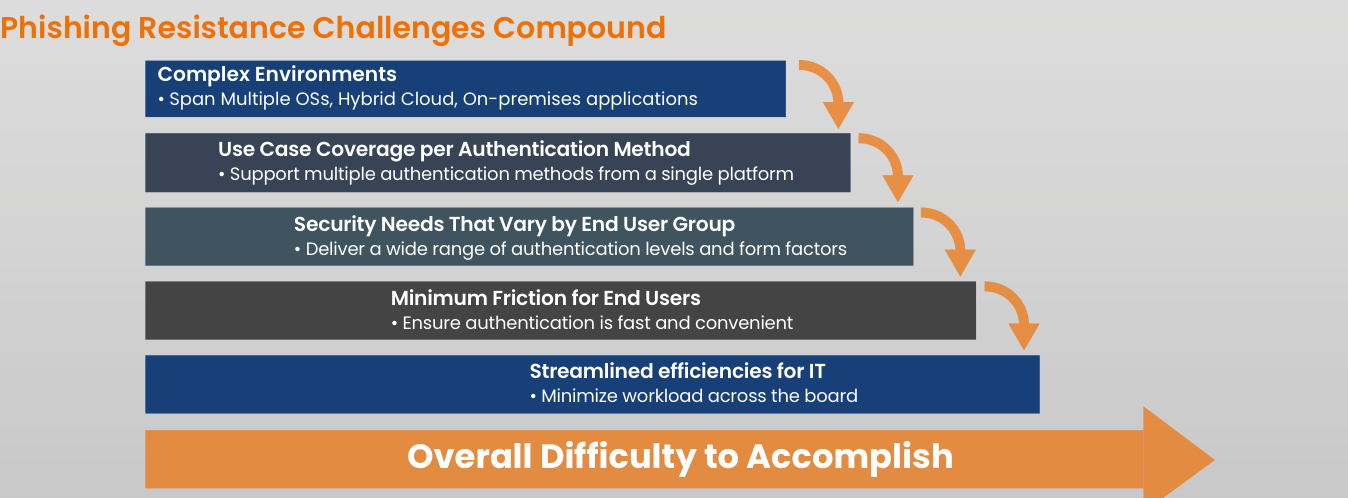
Phishingresistant authentication challenges build on each other, compounding implementation difficultiesfor agencies
Introducing Axiad Conductor
Axiad Conductor is a comprehensive,efficient, and secure authentication SaaS platform that eliminates silos acrossthe environment. Architected for best-practices security, it enables“mix-and-match” use of the Axiad Conductor product line. It can be applied inheterogeneous IT environments – e.g., organizations operating Windows, Mac, andLinux operating systems or with multiple existing IAM systems in place – allowingorganizations to remove gaps and inconsistencies in how they authenticateacross complex ecosystems, and ultimately to become more programmatic in theiroverall cybersecurity practices.
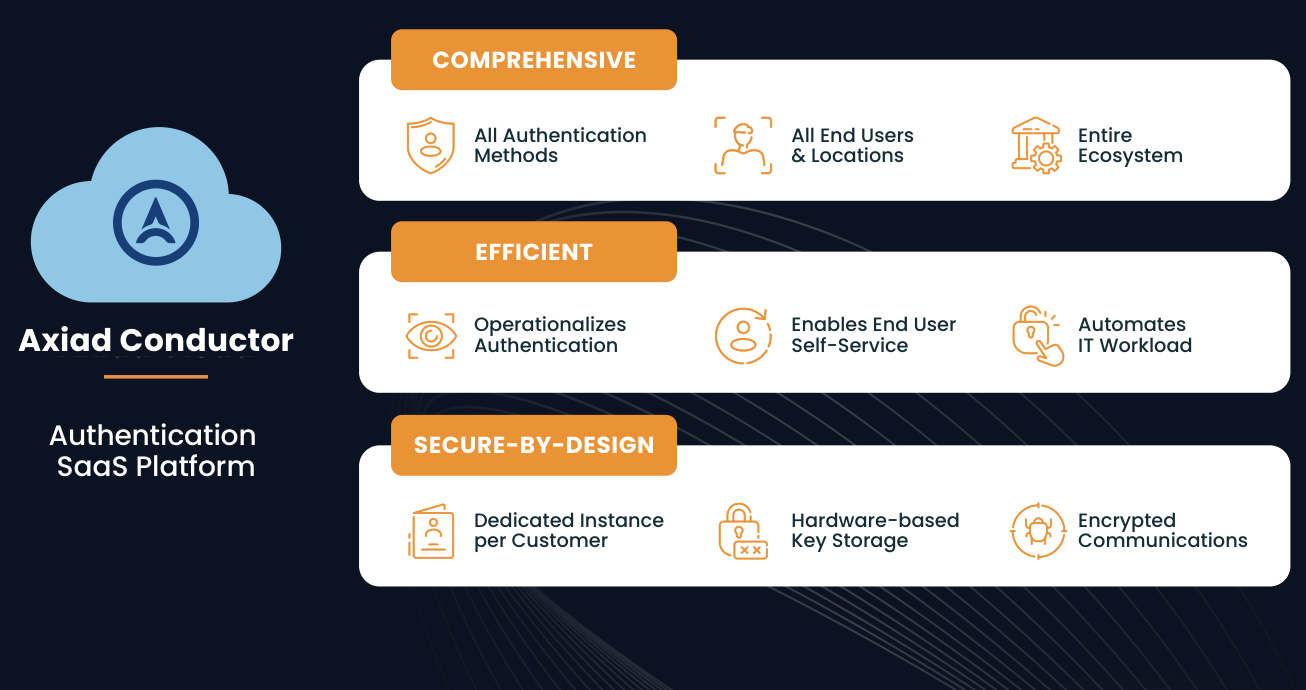
Capabilities
- Comprehensive: Supports allauthentication methods across users, machines, and more while interoperatingwith the entire Identity ecosystem
- Efficient:Streamlines and automates help desk workload, enables end user self- service,and minimizes overall IT overhead
- Secure-by-Design:Architecture designed with best-practices security including a private instancefor each customer, key storage in specialized hardware, and encryptedcommunications.
Pragmatic phishing resistance overview
As shown in the previous section, a keyadvantage of the Axiad Conductor platform is support for multipleauthentication methods including Certificate-Based Authentication (CBA) andFIDO passkey. This capability is of high value since Axiad estimates thatPIV/CIV cards, USB Keys, and Certificate-Based Authentication (CBA) will infuture handle 75% of use cases. FIDO passkey support provides future-proofing asAxiad estimates it will grow to 25% of use cases. (There are also use casesthat are supported by both authentication methods today such as Windowsworkstation authentication and likely soon such as MacOS workstationauthentication.)
Axiad believes that “Pragmatic PhishingResistance” – supporting best-of-breed authentication methods today such as CBAwhile futureproofing with FIDO passkey – is the best strategy for governmentagencies. This strategy handles today’s threats while increasing securitylevels over time to master tomorrow’s threats.
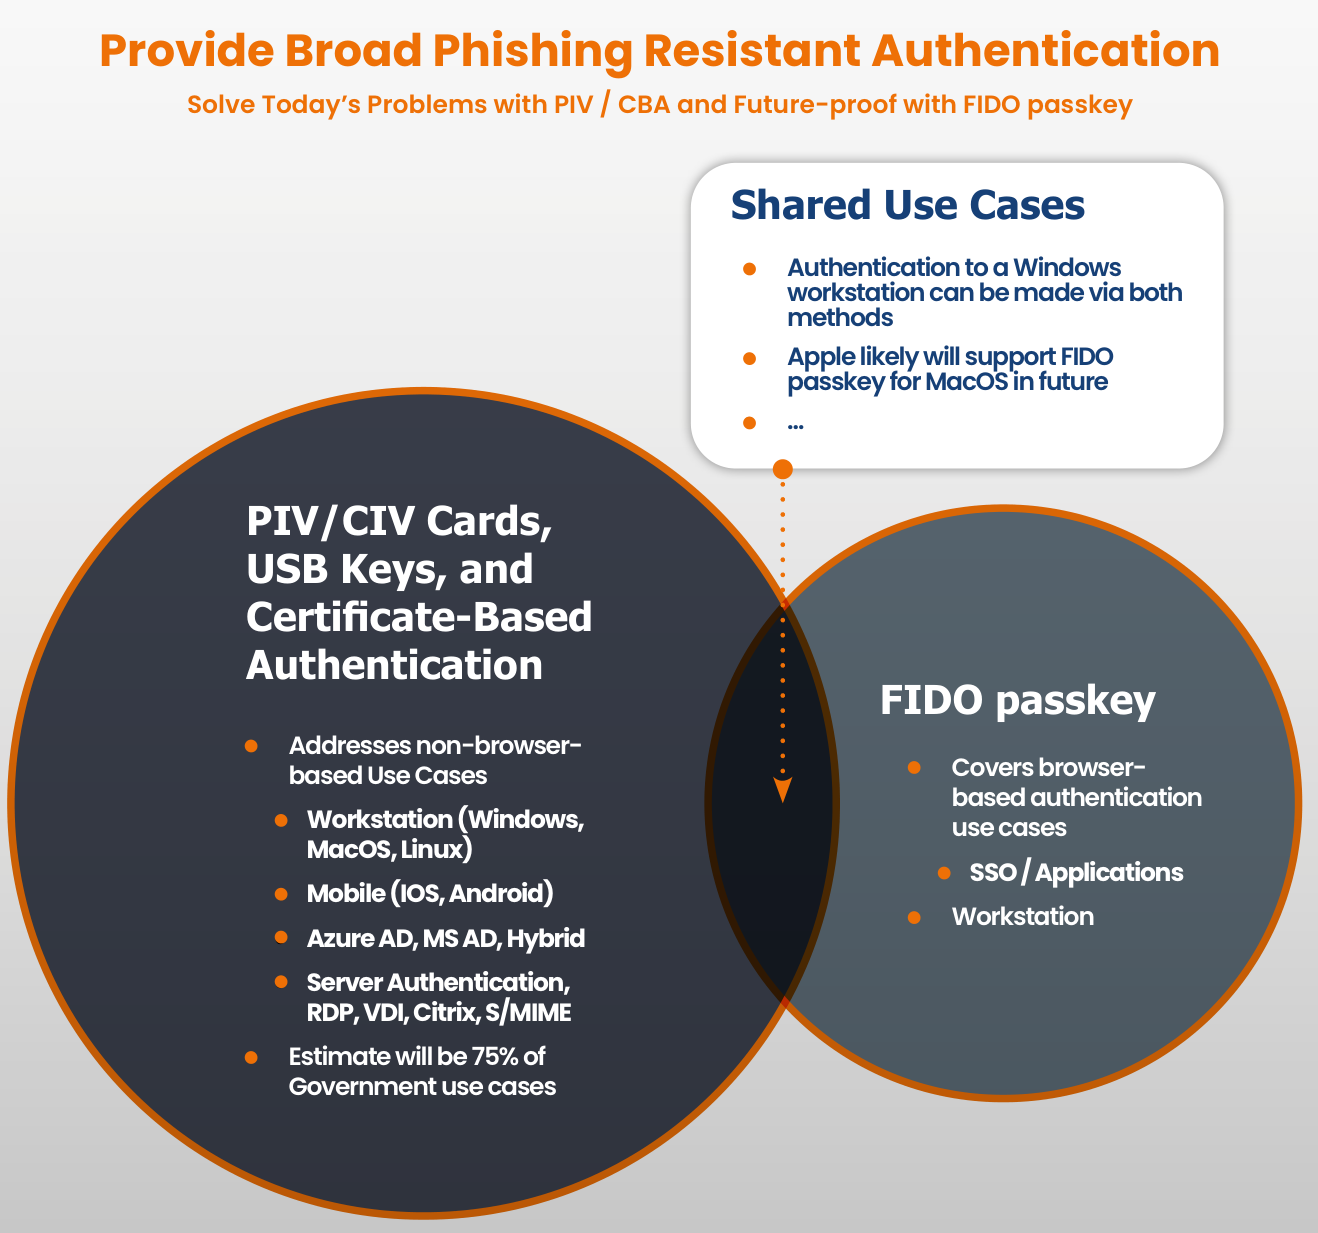
“Pragmatic Phishing Resistance” is the optimumstrategy today for agencies of all sizes
Pragmatic phishing resistance – twooptions
To best illustrate pragmatic phishingresistance, two options have been selected:
- The first – Enhance Security and Minimize Disruption– describes how phishing-resistant authentication can be added to an existingenvironment without changing how authentication operates among 1 to manyIdentity Access Management (IAM) vendors.
- The second – Maximize Security and Get More from Investments – outlines ascenario where authentication is centralized by Axiad, thereby extendingexisting investments in IAM vendors’ products as well as infrastructurecomponents provided by Microsoft.
Option 1 – Enhance Security andMinimize Disruption
With this option, Axiad handles theauthentication management lifecycle for the organization’s choice of phishing-resistantauthenticators. Key attributes:
- Challenges: Challengesexperienced by government agencies include:
- Siloed Infrastructure: Siloed authenticationtypically results in poor end user experience as well as increases the securityexposure surface.
- Enrollment and Renewal: Phishing-resistantauthenticators are challenging for IT to roll out and periodically renew due tohigh manual effort and support needs.
- Skills Shortage: Key authenticationinfrastructure skills, such as Certificate-Based Authentication and Public KeyInfrastructure (PKI), are in short supply.
- Pragmatic Phishing Resistance: For thisscenario, Axiad Conductor’s Certificate-Based Authentication (CBA) for IAM“bolts on” to the existing infrastructure including IAM systems. Credentialsthat can be leveraged are Certificates and Windows Hello for Business. Keyattributes:
- End user self-services CEAR: CredentialEnrollment and Account Recovery (CEAR) is performed by end users inself-service mode, thereby offloading IT.
- Phishing resistance is fully enabled: By usingstrong authenticators consistently across the environment, phishing resistancebecomes the baseline security across the agency.
- Current: Operational controls keep Axiad CBAfor IAM in sync with each IdP.
- Business Outcomes
- Non-disruptive: Since authentication isperformed by the installed system (IAM, Azure AD, and Microsoft AD), existingsystems are not disrupted.
- Maximizes Acceptance: With helpfulself-service utilities replacing onerous and lengthy calls to Help Desk, enduser acceptance is maximized.
- IT Productivity: By being offloaded by self-servicefor end users and made more efficient with specialized utilities, ITproductivity is significantly enhanced.
- Increases Investment Return: By improvingsecurity without requiring upgrades, this option increases the return oninvestment for both infrastructure (e.g., Microsoft AD) and IAM products.
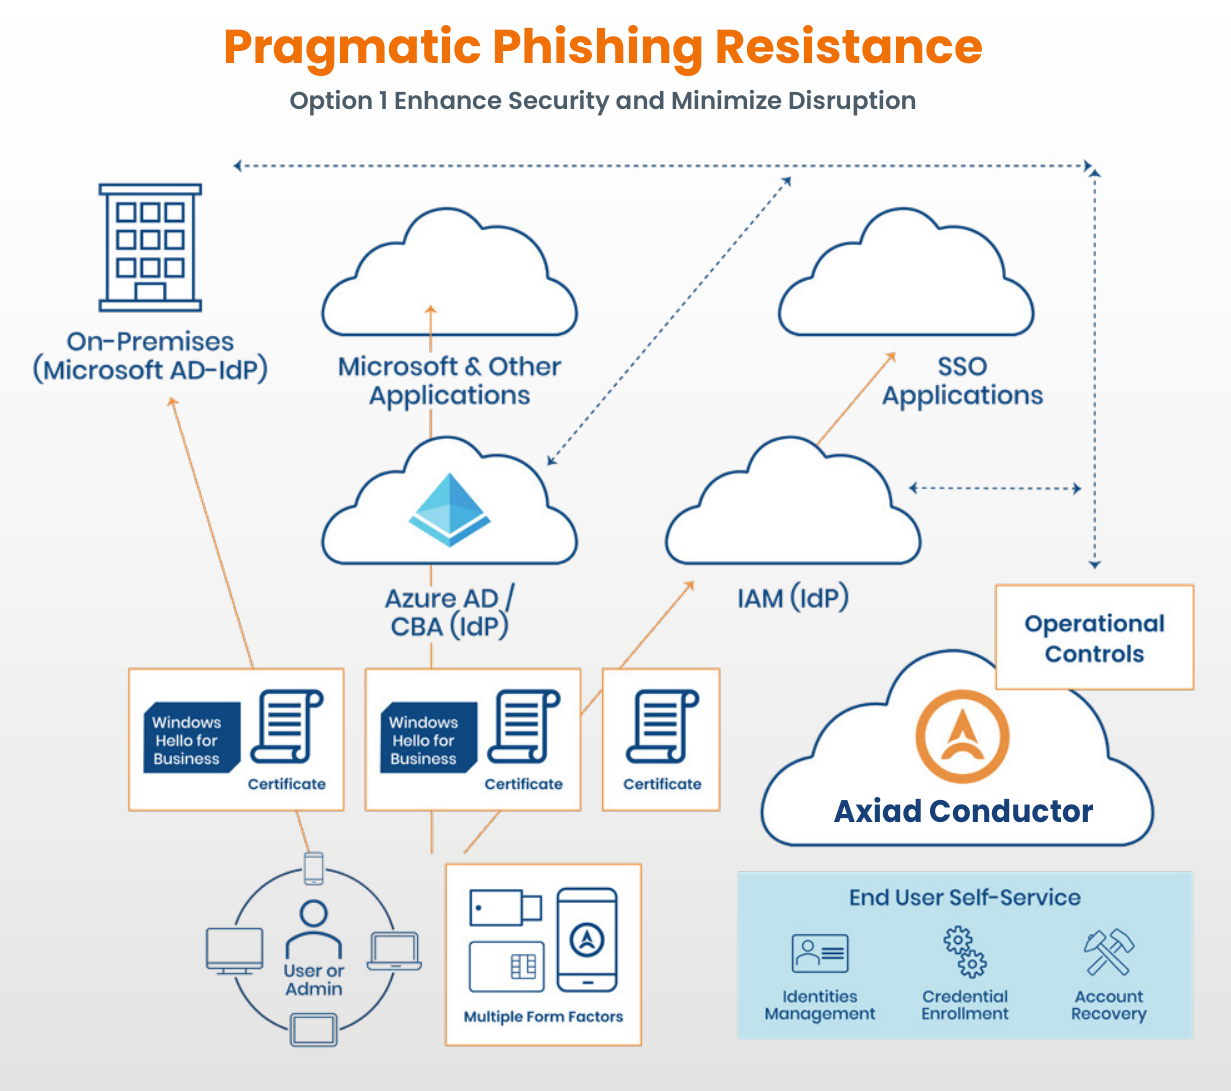
Phishing-resistantauthentication can be “bolted on” to upgrade authentication for on-premises and IAMsystems
Option 2 – Maximize Security and GetMore from Investments
With this option, Axiad adds a unifiedIdentity Provider (IdP) capability and an additional authenticator option (FIDOpasskey) to the authentication management lifecycle from option 1.
Keyattributes:
- Challenges:Challenges experienced by government agencies include:
- Siloed Infrastructure: Siloed authenticationtypically results in poor end user experience as well as increases the securityexposure surface.
- Enrollment and Renewal: Phishing-resistantauthenticators – including FIDO passkey – are challenging for IT to roll outand periodically renew due to high manual effort and support needs.
- Skills Shortage: Key authenticationinfrastructure skills, such as Certificate-Based Authentication and Public KeyInfrastructure (PKI), are in short supply.
- Pragmatic Phishing Resistance: For thisscenario a combination of FIDO passkey and Certificate-Based Authentication(CBA) are the optimal authentication methods. Credentials that can be leveragedare Certificates, FIDO log-on, and Windows Hello for Business. Key attributes:
- End user self-services CEAR: CredentialEnrollment and Account Recovery is performed by end users in self-service mode,thereby offloading IT.
- Phishing resistance is fully enabled: By usingstrong authenticators consistently across the environment, phishing resistancebecomes the baseline security across the agency.
- Current: Operational controls keep AxiadConductor in sync with each IdP.
- Business Outcomes
- Maximizes Flexibility: With an authenticationplatform that supports a broad range of phishing-resistant authenticators andcredentials, the organization can ensure secure authentication for every need.
- Increases Investment Return: By improvingsecurity without requiring upgrades, this option increases the return oninvestment for both infrastructure (e.g., Microsoft AD) and IAM products.
- Maximizes Acceptance: With helpfulself-service utilities replacing onerous and lengthy calls to Help Desk, enduser acceptance is maximized.
- IT Productivity: By being offloaded byself-service for end users and made more efficient with specialized utilities,IT productivity is significantly enhanced.
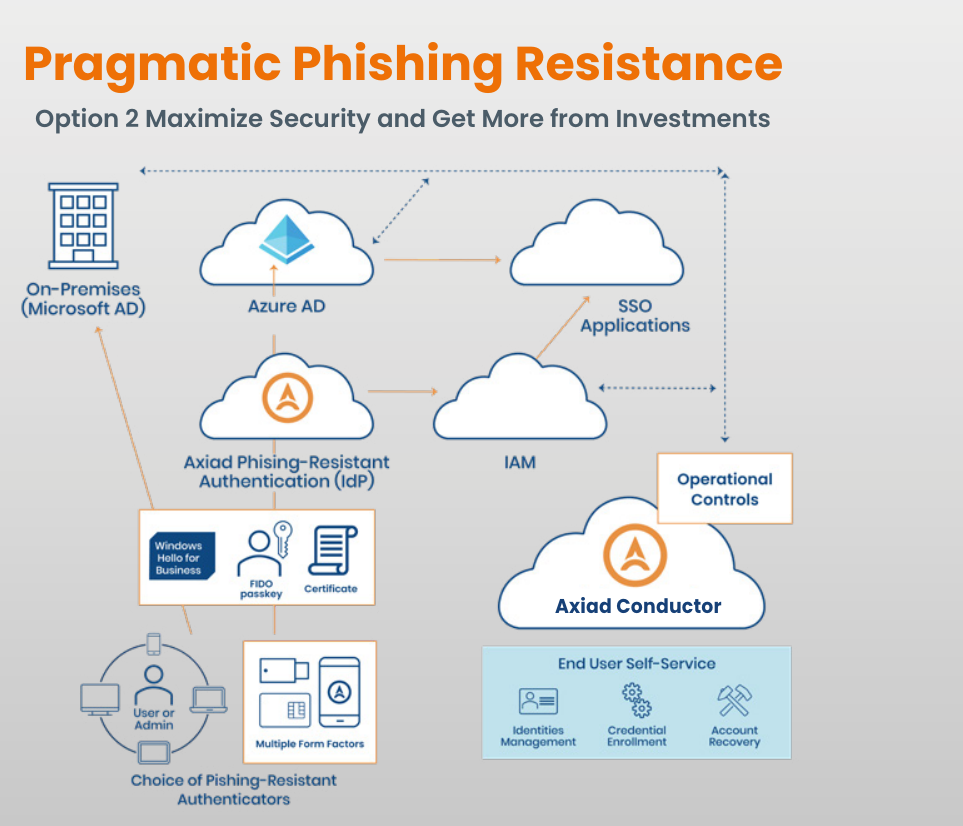
Centralizedphishing-resistant authentication increases security and adds life to existing infrastructure andIAM investments
Unique authentication managementcapabilities
As of this writing, Axiad’s approachprovides capabilities that cannot be matched elsewhere:
- ComplexEnvironment Support: Axiad supports complex environments across OSs (Windows,MacOS, and Linux), hybrid environments (Microsoft AD, Azure AD), and multipleIAMs (such as Okta, Ping Identity, and Azure AD).
- Full Use Case Coverage: The Axiad ConductorPlatform supports multiple authentication methods seamlessly includingCertificate-Based Authentication (CBA), FIDO passkey, Phishing-Resistant MFA,and PKI.
- Authentication Matched to Department Need:Axiad supports varying authentication levels by department such as PIV cardsfor the Finance team and USB Keys for everyone else.
- High End User Satisfaction: Axiad enables endusers to self-service the authentication management lifecycle from initialenrollment through account recovery, thereby minimizing end user friction and increasingsatisfaction.
- Maximized IT Efficiencies: IT efficiencies aremaximized via leveraging Axiad’s utilities for authentication lifecyclemanagement and via enabling end users to self-serve most of theirauthentication needs.
Benefits for this use case
Continuing the balancing analogy from theintroduction, these pragmatic phishing resistance use cases provide a win-winperspective from the perspective of the End User, IT, and the budget.
Maximize End User Security
Passwordless, phishing-resistant authenticationmaximizes end user security while minimizing friction
Maximize IT Efficiency
By operationalizing authentication intoplaybooks, IT efficiency is maximized
Minimize Security Overhead
By minimizing breach costs and bystreamlining effort for end users and IT, overall security overhead isminimized
About Axiad
Axiad is an identity security companytackling the growing threat of compromised credentials, which drive over 70% ofenterprise breaches. The sprawl of human and non-human identities across organizationsilos creates security blind spots that existing tools fail to secure. Axiadtackles this problem head-on, detecting identity risks and poor credentialhygiene across systems, providing actionable insights, and enhancing securitywithout needing a complete overhaul. Axiad makes identity simple, effective,and real. Discover more at or follow us on .


Back

Back
Back