




Passwordless for Air Gapped and CriticalEnvironments
Overview of use case
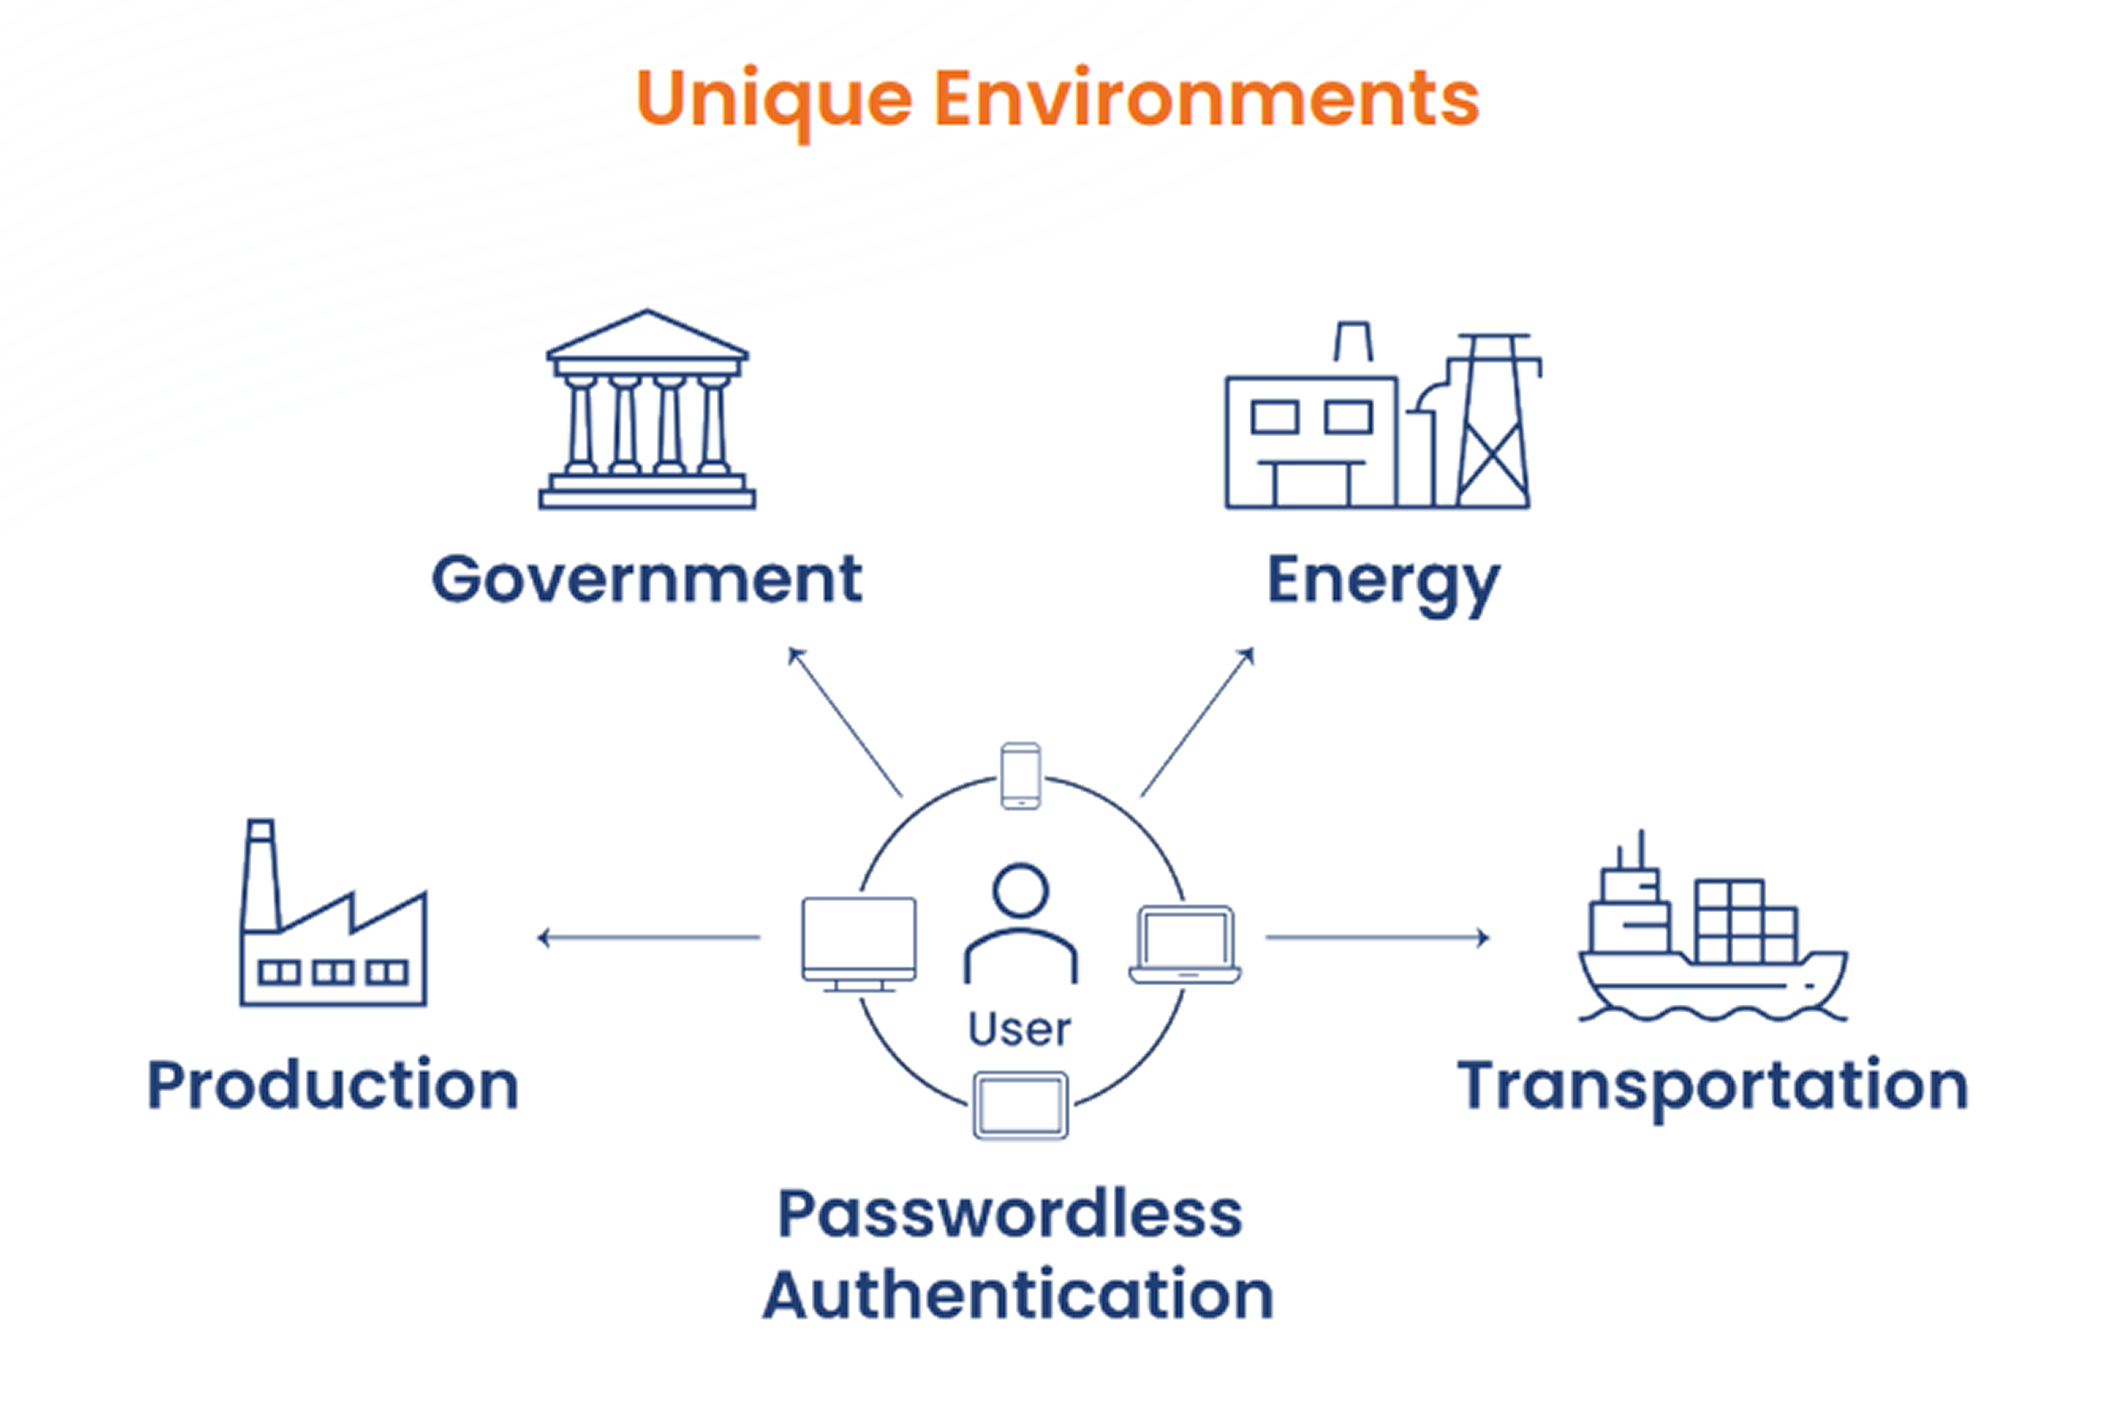
Government agencies, critical infrastructureorganizations, and defense contractors are automatingmonitoring, detection, and production controls withincreasingly sophisticated systems. However, theseadvances are accompanied by a cost: geometricincrease in the security exposure surface and inpotential downsides (such as operational disruption)should threat actors compromise the system.To minimize exposure, these “frontline” (using theGartner term1) systems are implementing air gappingvia a production network that is fully isolated frompublic networks. Due to the high stakes of acompromise, strong passwordless authentication isrequired for government agencies by the White HouseExecutive Order (EO) 14028 on Improving the Nation’sCybersecurity2 and Fact Sheet3 for these systems.Strong passwordless authentication in air gapped and critical infrastructure environments presents uniquechallenges for authentication management. Government agencies, critical infrastructure organizations, and defensecontractors need passwordless authentication management that overcomes these challenges while leveragingcurrent on-premises environments.
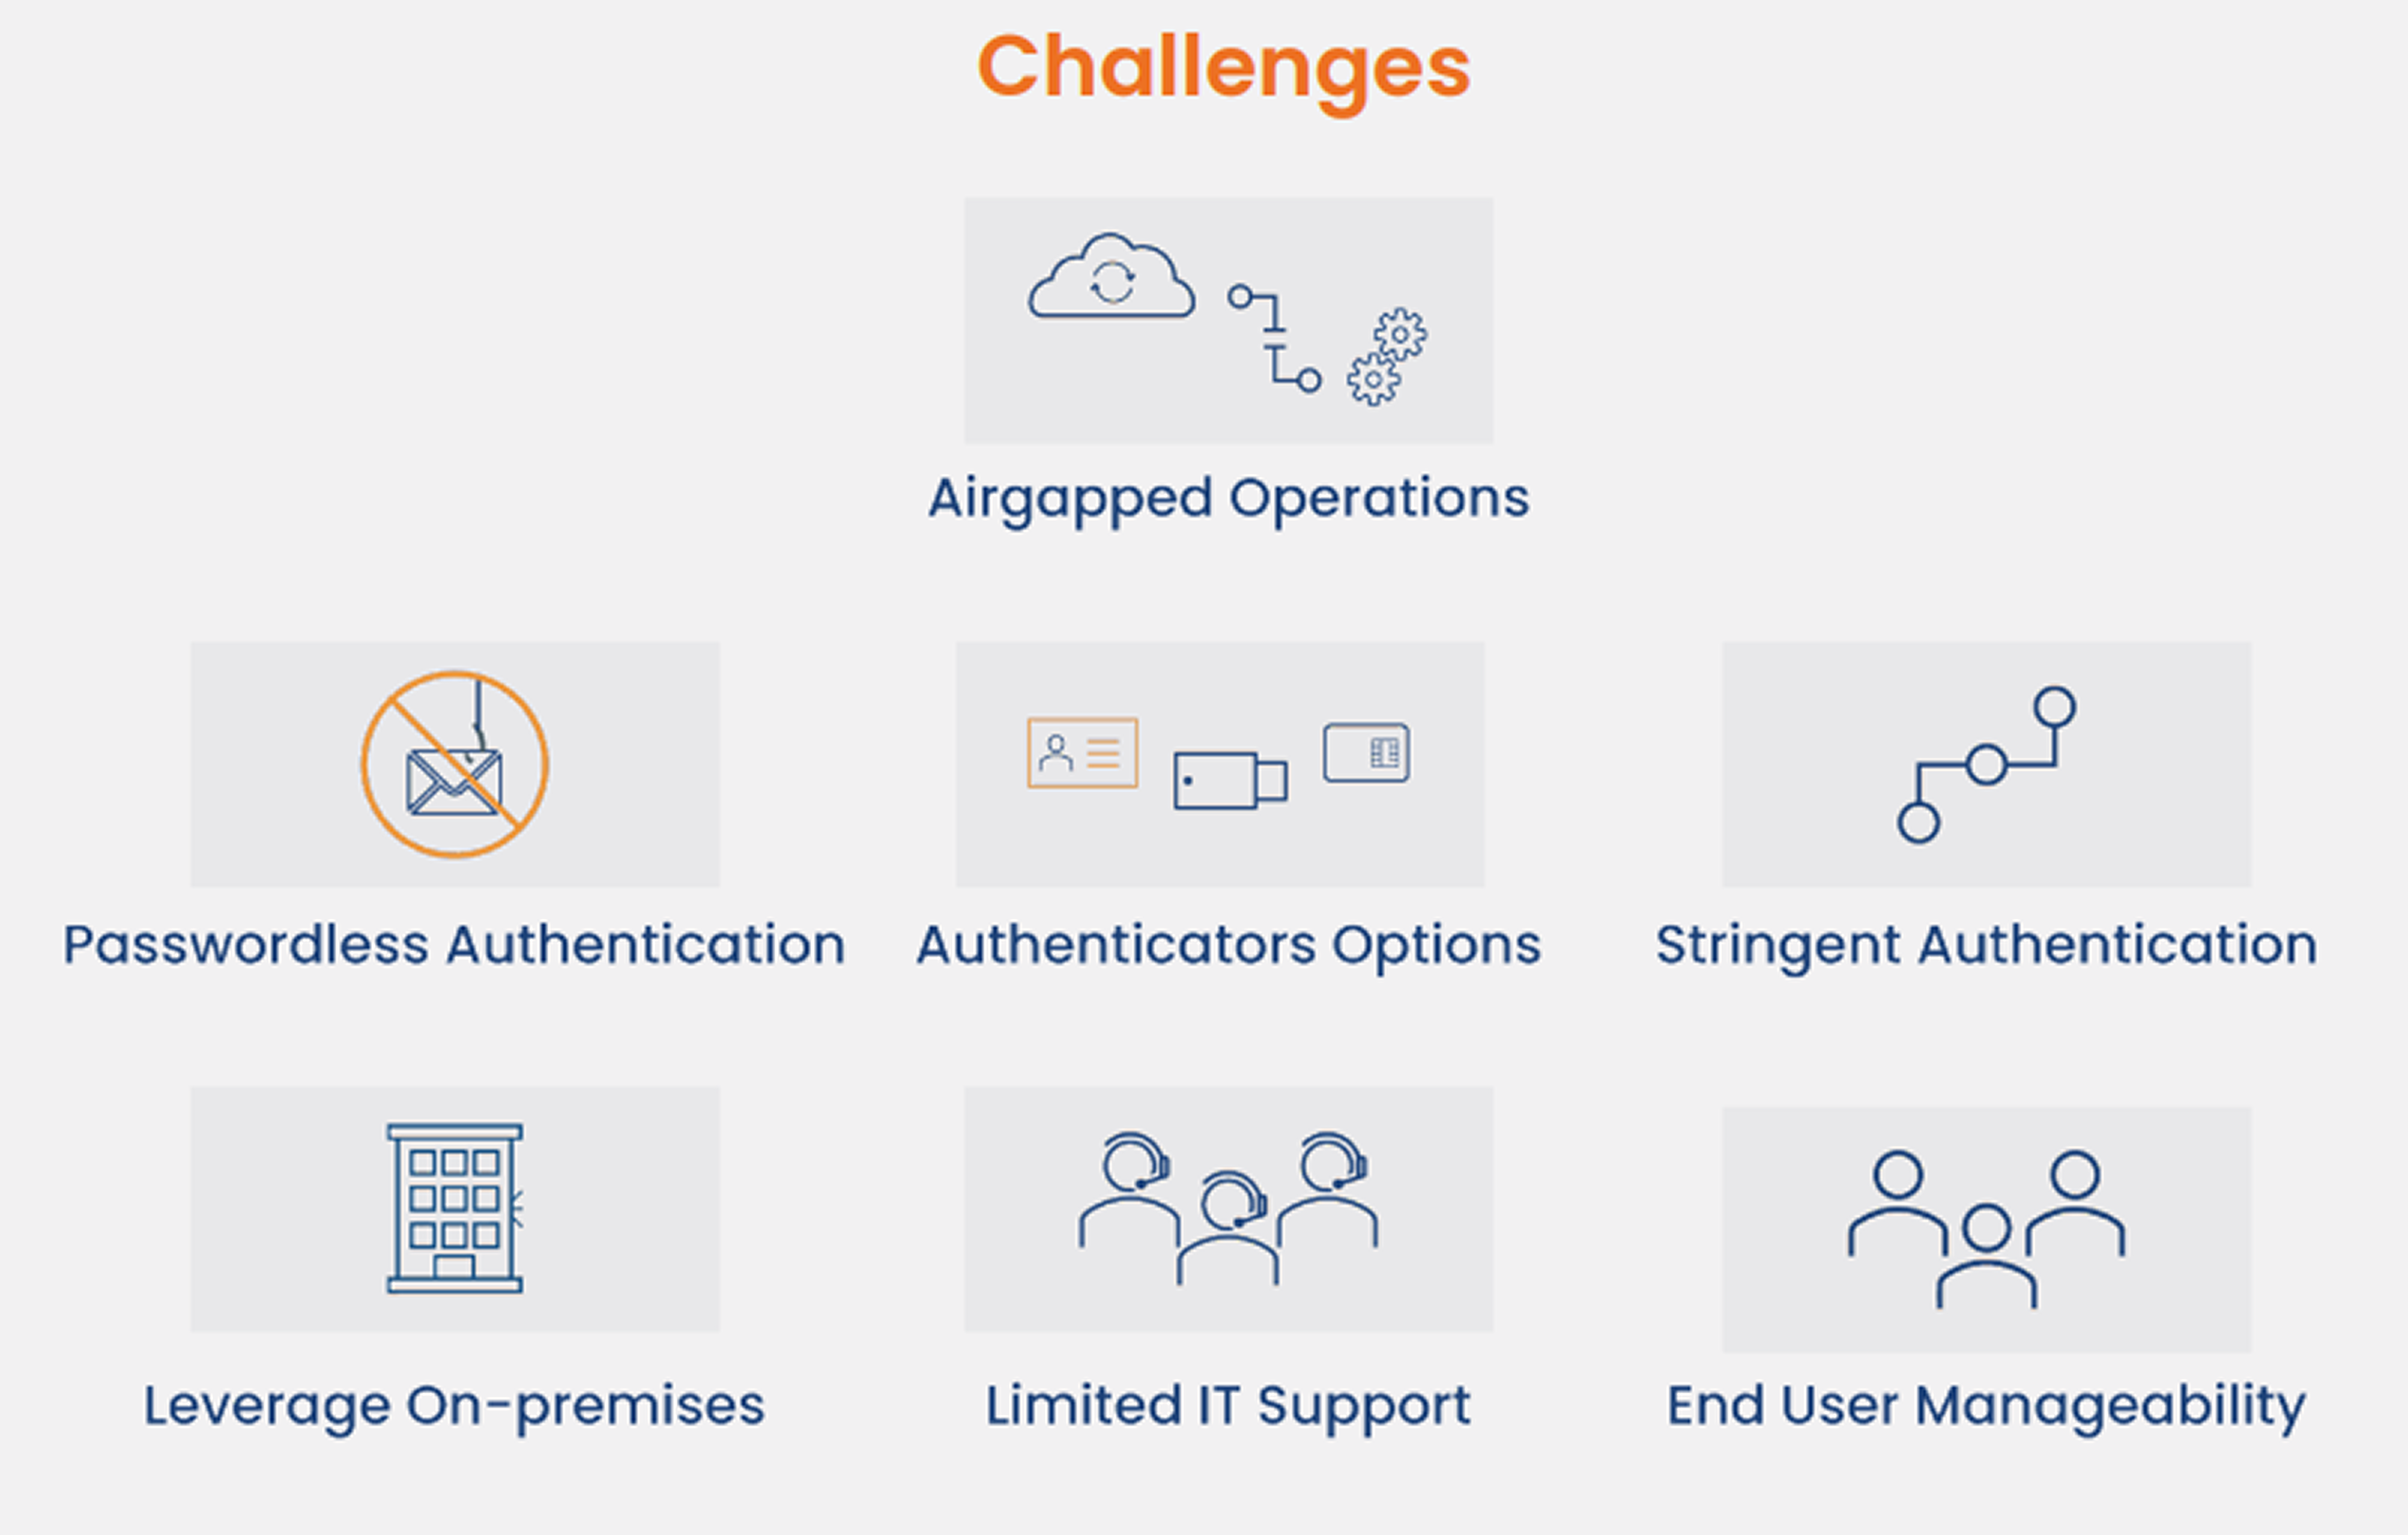
Challenges
As they cannot leverage cloud-based Identity products – such as Microsoft Entra ID or Identity and AccessManagement (IAM) products – air gapped environments present unique challenges for authentication management:
- Fully Air Gapped Operations: Must be installed, maintained, and run without a networkconnection.
- Passwordless Authentication: To provide passwordless phishing resistant authentication, supportfor dedicated physical (such as PIV card and USB Key) and platform (such asVirtual Smart Card and passkey) authenticators and credentials must beprovided.
- Authenticator Options: Arecent Gartner report indicates that many frontline environments (oil rigs,manufacturing, and even retail) prohibit the use of smart phones. To span awide range of device readers, multiple authenticator form factors must besupported.
- Stringent Authentication Needs: To comply with security standards, need to authenticate toworkstation prior to application authentication.
- Leverage On-premises Environment: An authentication management approach must leverage the currenton-premises environment.
- Limited IT Support: Thesystem must operate without reliance on on-site IT or extensive Help Desksupport.
- End User Manageability:The system must minimize end user friction via usability and self-servicecapabilities.
Unique Requirements of Air GappedEnvironments Lead to Unique Challenges
Introducing Passwordless for Air Gapped and CriticalEnvironments
Axiad Unified Credential Management System(UCMS) provides unified, consistent, and efficient credential management forend users. A UCMS package, Passwordless for Air Gapped and CriticalEnvironments, is deployed as an air gapped on-premises offering for criticalinfrastructure organizations, government agencies, and defense contractors. Withsupport for strong authentication credentials across the organization, thepackage handles the authentication management lifecycle at scale. The packagehelps organizations with very high security needs or very significanton-premises application investments to achieve passwordless authenticationseamlessly.
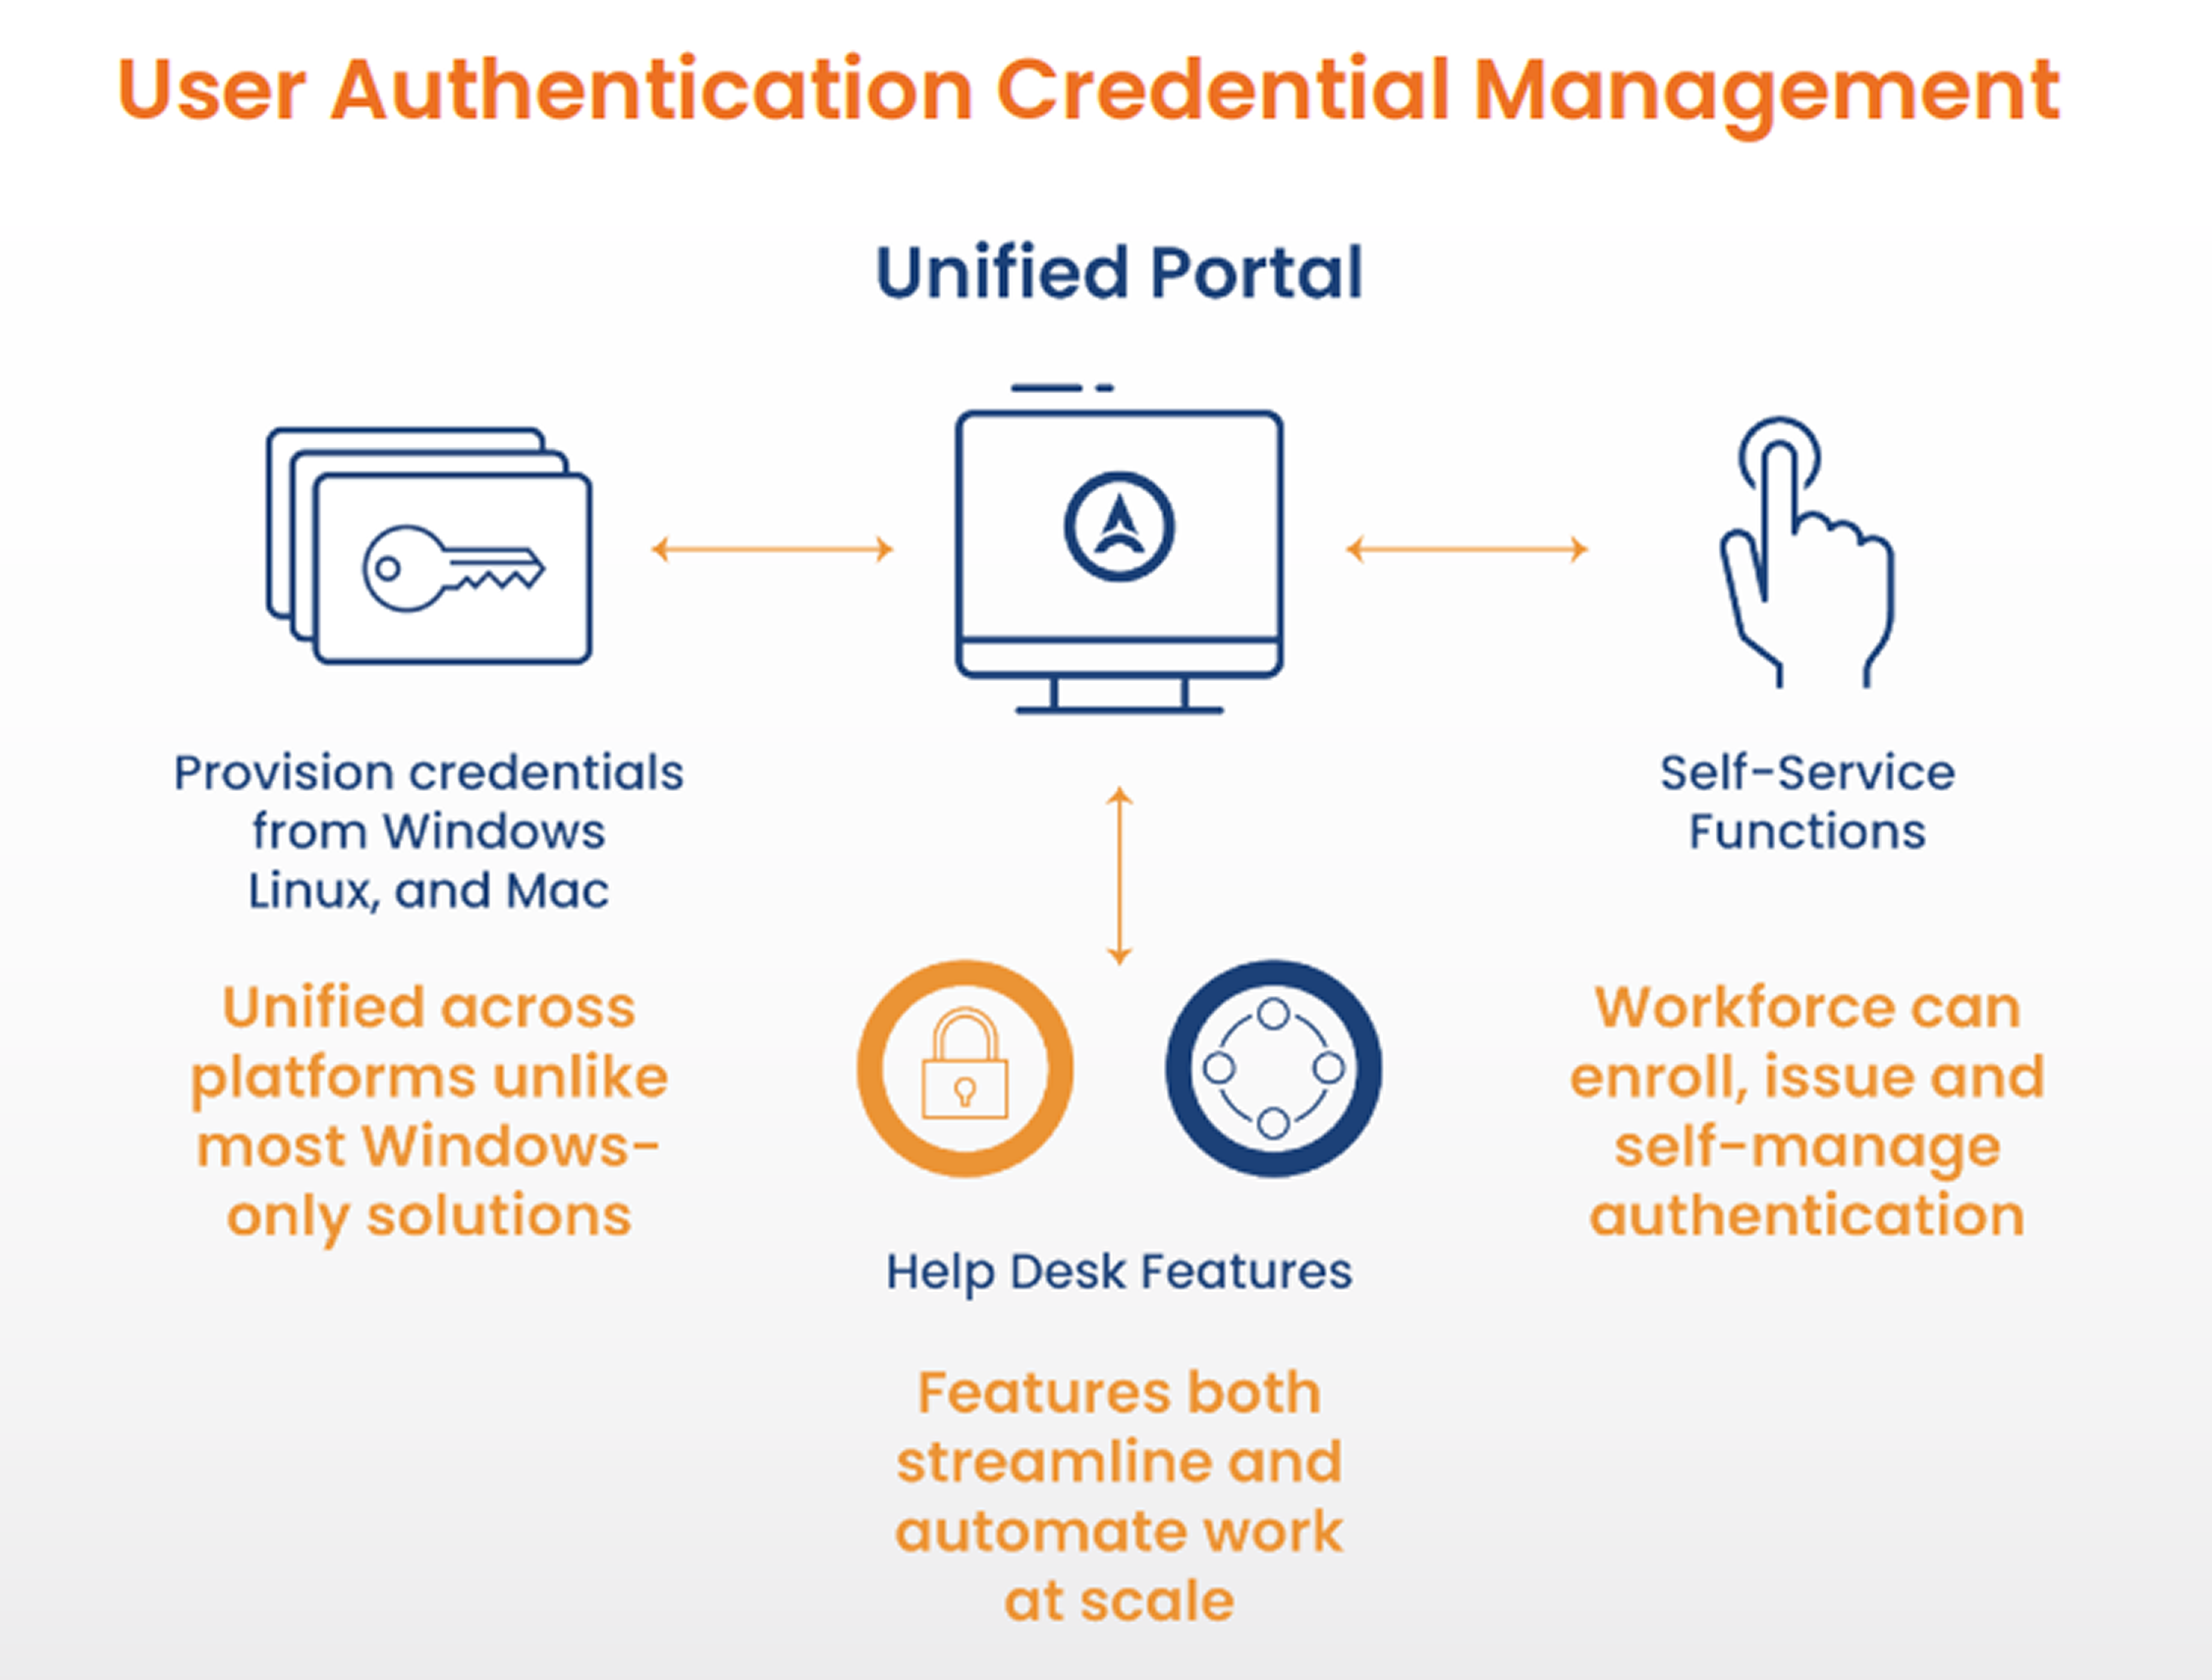
Unified, Consistent, and Efficient end userauthentication management lifecycle, deployed as an on-premises product
- Unified: A single packagemanages all end user authentication credentials throughout their lifecycle.
- Consistent: Credentialsare consistent across OSs, applications, services, and more.
- Efficient: Unified Portalstreamlines and automates workload for IT and end users
Passwordless for Air Gapped and CriticalEnvironments is architected for air gapped on-premises environments. Initialinstallation and updates are performed from a thumb drive. The package enablespasswordless authentication across the existing on-premises environmentincluding Microsoft AD, Microsoft CA, and more.
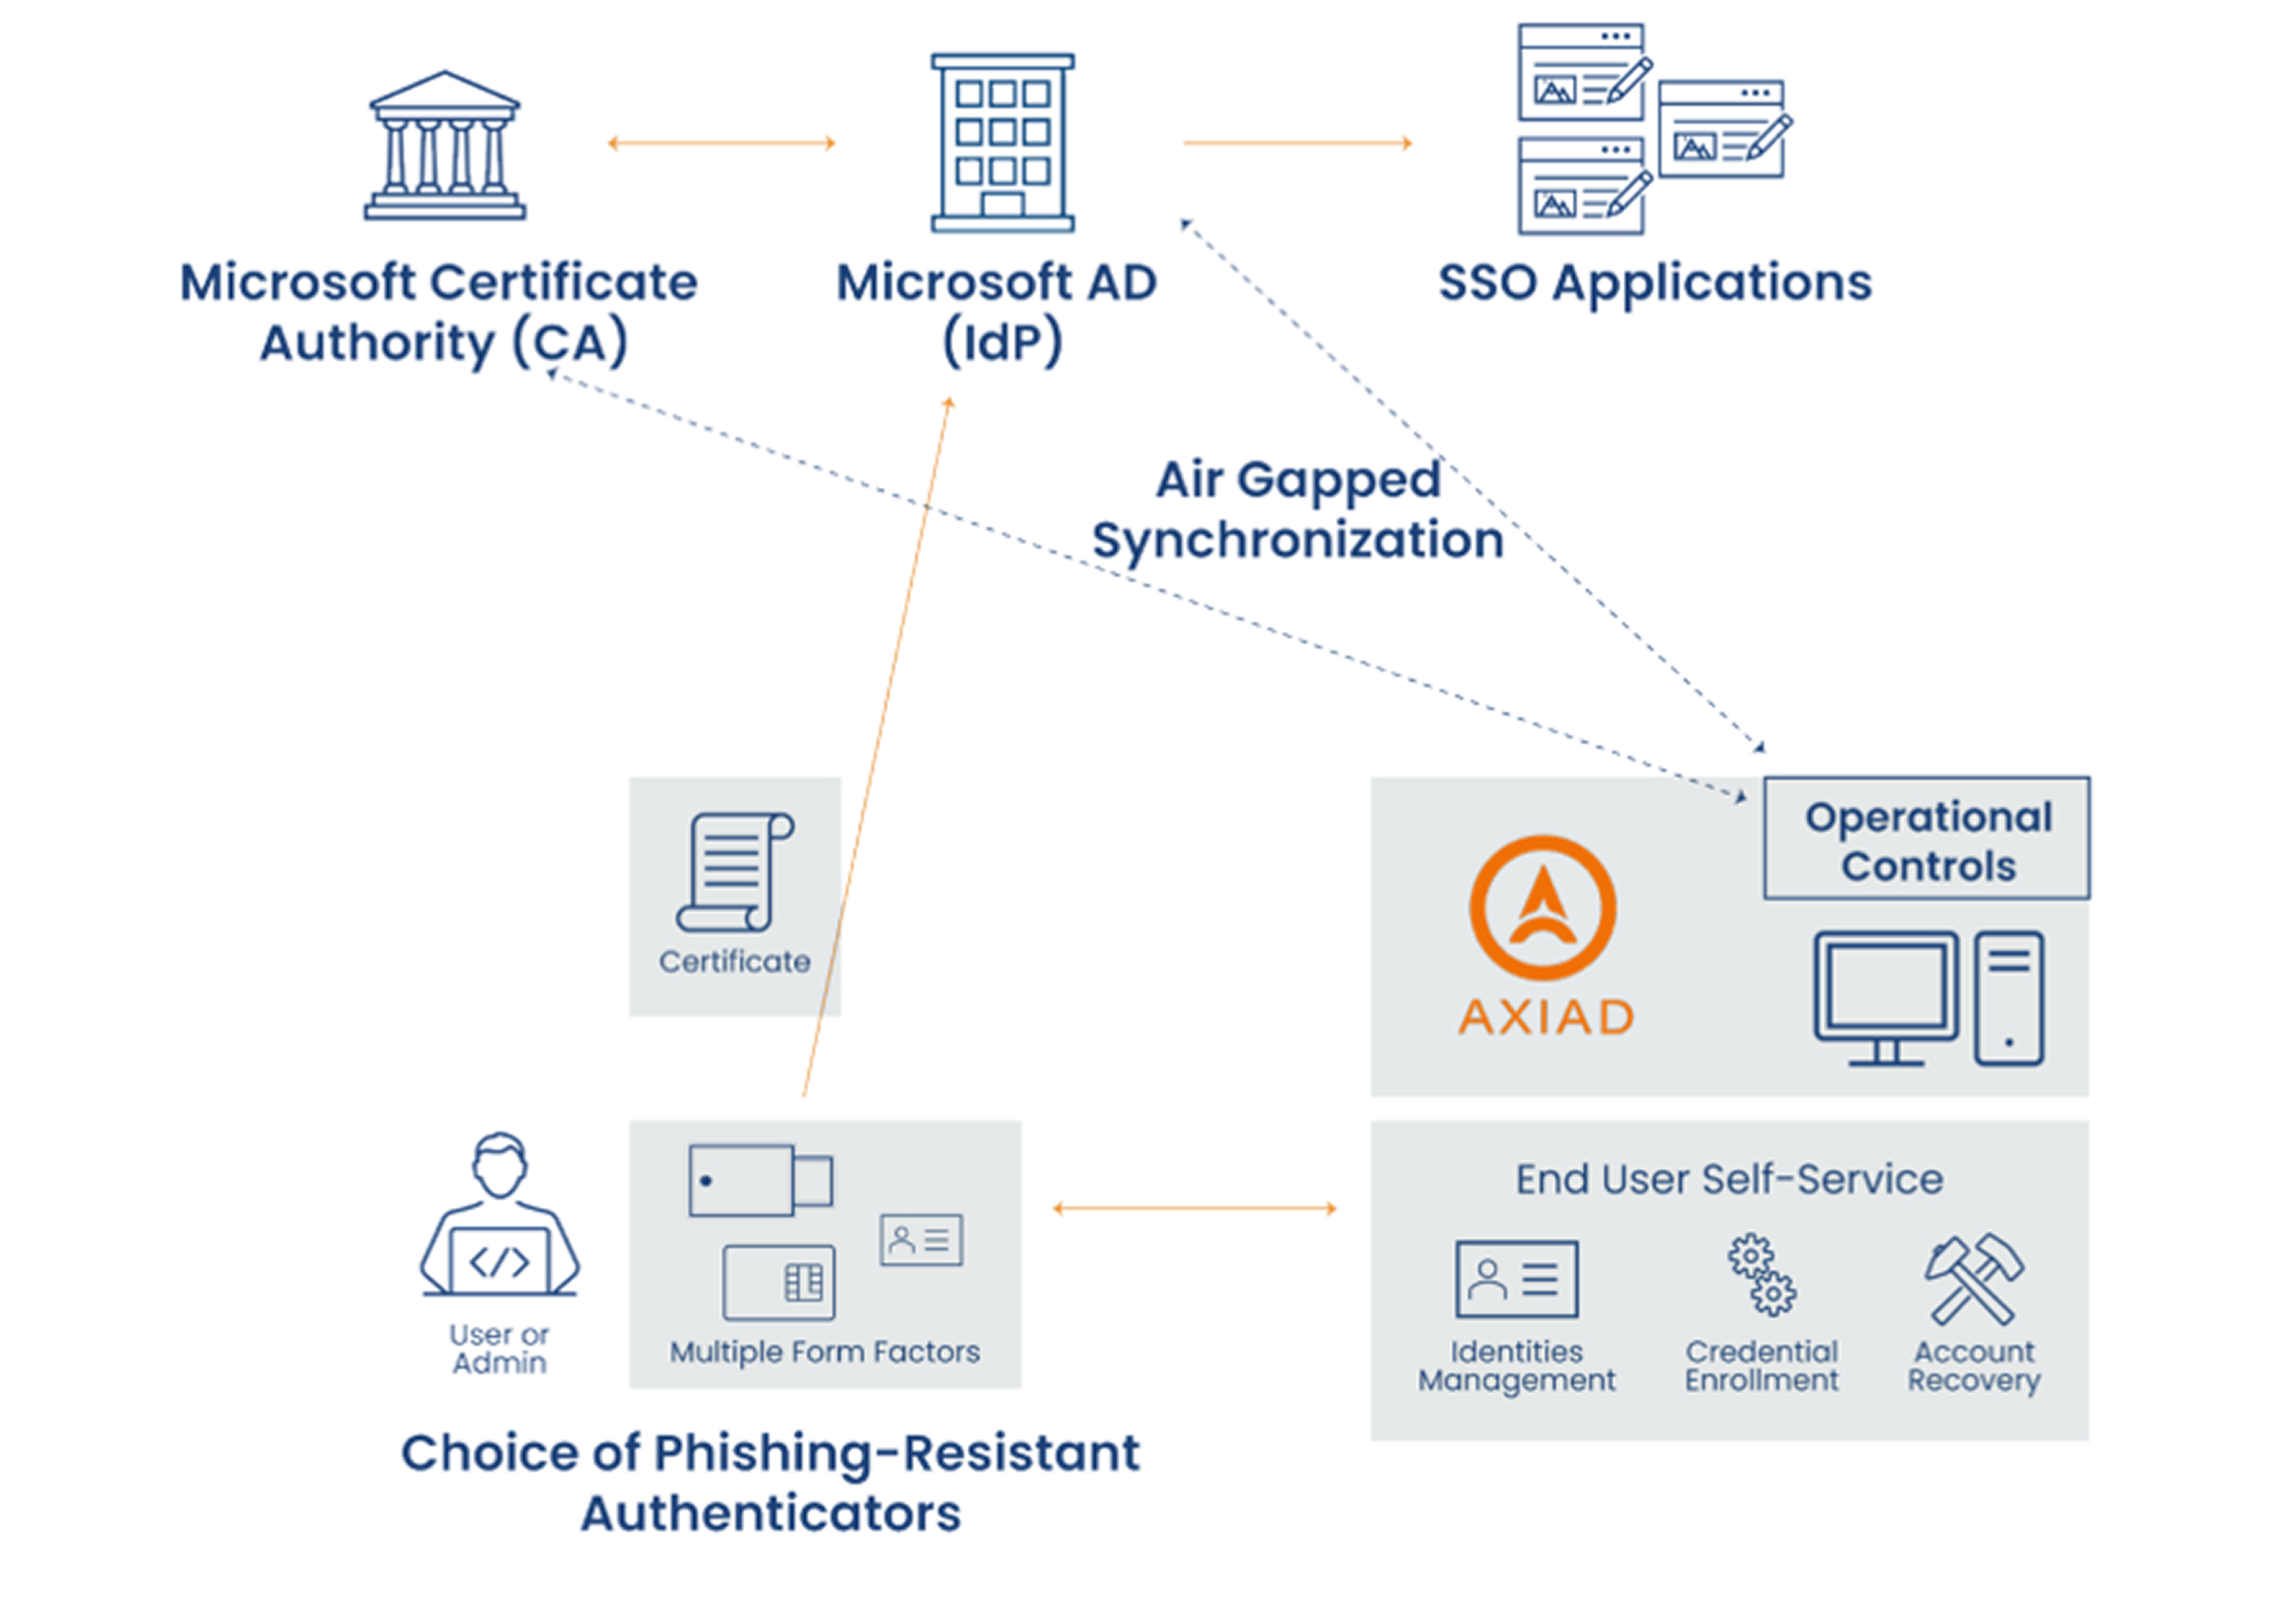
Initial and Ongoing Operations
- Installation and operations areoffline and air gapped
- Syncs with Microsoft CA andMicrosoft AD via air gapped network only
Authentication is Unchanged
- End user self-services enrollmentof authenticator(s) and provisioning of credential(s)
- Passwordless authentication isfully enabled without modifying how authentication is performed by Microsoft AD
Meeting the Needs
Passwordless for Air Gapped and CriticalEnvironments fully meets the needs of air gapped environments for governmentagencies, critical infrastructure organizations, and defense contractors.
- Fully Air GappedOperations: Must be installed, maintained, and runwithout a network connection.
- Passwordlessfor Air Gapped and Critical Environments has proven success in running in airgapped environments. It does not require a public connection to operate. Onsitepersonnel can maintain the package intermittently by installing updates from athumb drive.
- Passwordless Authentication: To provide passwordless phishing resistant authentication, supportfor dedicated physical (such as PIV card and USB Key) and platform (such asVirtual Smart Card) authenticators and credentials must be provided
- The packagesupports a full range of authenticators including dedicated physical (PIV card,Smart Card, and USB Key) and platform (Virtual Smart Card) authenticators andcredentials. Certificatebased approaches such as Certificate-BasedAuthentication (CBA) are also supported.
- Authenticator Options: To span a wide range of device readers, multiple authenticator formfactors must be supported.
- As discussedabove, many frontline environments prohibit the use of smart phones and not allmachines are able to read each authenticator. As a result, authentication mustsupport a full range of authenticators. Passwordless for Air Gapped andCritical Environments enables multiple authenticators, each with differentcredentials to be assigned and managed per end user. That way, any mix of ongoingand temporary (project-based) authentication can be managed.
- More StringentAuthentication Needs: To comply with securitystandards, need to authenticate to workstation prior to applicationauthentication.
- Many existingauthentication approaches do not encompass workstation authentication. Asecurity gap is the result since the workstation is not secured with apasswordless, phishingresistant authenticator. Passwordless for Air Gapped andCritical Environments includes an AirLock feature that ensures that the enduser has set up the authenticator prior to being able to access applications.Further, AirLock ensures that the end user authenticates to the workstationeach time prior to being able to access applications either standalone or viaSSO (via Microsoft AD).
- Leverage CurrentEnvironment: An authentication management approachmust leverage the current on-premises environment.
- The on-premises ecosystem is a different software stack from the cloud ecosystemand typically leverages the Microsoft ecosystem. Passwordless for Air Gappedand Critical Environments fully leverages Microsoft AD, Microsoft CA, WindowsServer, and other components of the on-premises environment to ensureauthentication is highly secure and consistent, all without requiring upgrades.
- Limited IT Support: The system must operate without reliance on on-site IT support.
- Since thesystem must be able to operate without reliance on on-site IT support, Axiadprovides upgrades and maintenance via thumb drives that can be installed bylocal personnel. Axiad support provides real-time guidance for installingupgrades and maintenance.
- End User Manageability: The system must minimize end user friction via usability andself-service capabilities.
- Since IT istypically not onsite in air gapped environments, end users must be able toself-service authentication management. Passwordless for Air Gapped andCritical Environments includes the AirLock and MyCircle features. Thesefeatures enable the entire Credential Enrollment and Account Recovery (CEAR) lifecycleto be self-serviced by the End User. The End User can select one or moreauthenticators and enroll the appropriate credentials (such as FIDO passkeysand Certificates) on each. Thereafter, AirLock provides reminders to renewcredentials via the Axiad Unified Portal. Finally, MyCircle ensures accountrecovery can be performed by getting approval from a designated “circle oftrust” rather than via a lengthy phone call to Help Desk.
Unique Authentication Management Capabilities
As of this writing, Axiad’s approachprovides capabilities that cannot be matched elsewhere:
- Air Gapped Operations:Provides full functionality while isolated from public-facing networks.
- Non-disruptive: Does notrequire changes to existing authentication systems, either for the workstationor applications.
- Unified: A single approachserves all end user authentication credentials, everywhere across theenvironment.
- Consistent: Credentialsare consistent across OSs, applications, services, and more.
- Efficient Credential Management: Passwordless deployment and account recovery processes are highlyefficient.
- Unified Portal: Provides asingle pane of glass for Users and IT with utilities that both streamline workand automate tasks.
- Self-Service Features:Features such as AirLock and MyCircle empower the workforce to enroll, issue,and self-manage their authenticators and credentials.
Unique capabilities provide superiorauthentication management in air gapped environments
Benefits for this Technical Brief
Maximize Security
Passwordless authentication eliminatespasswords that can be compromised and used in attacks
End User Acceptance
By providing end user selfservice andintuitive utilities, end user acceptance is maximized
Minimize Security Overhead
By streamlining effort for end users andIT, overall security and remediation overhead is minimized
About Axiad
Axiad is an identity security companytackling the growing threat of compromised credentials, which drive over 70% ofenterprise breaches. The sprawl of human and non-human identities acrossorganization silos creates security blind spots that existing tools fail to secure.Axiad tackles this problem head-on, detecting identity risks and poorcredential hygiene across systems, providing actionable insights, and enhancingsecurity without needing a complete overhaul. Axiad makes identity simple,effective, and real.
Discover more at axiad.com or follow us on LinkedIn.


Back

Back
Back