




Interim and Non-PIV authentication
Overview of use case
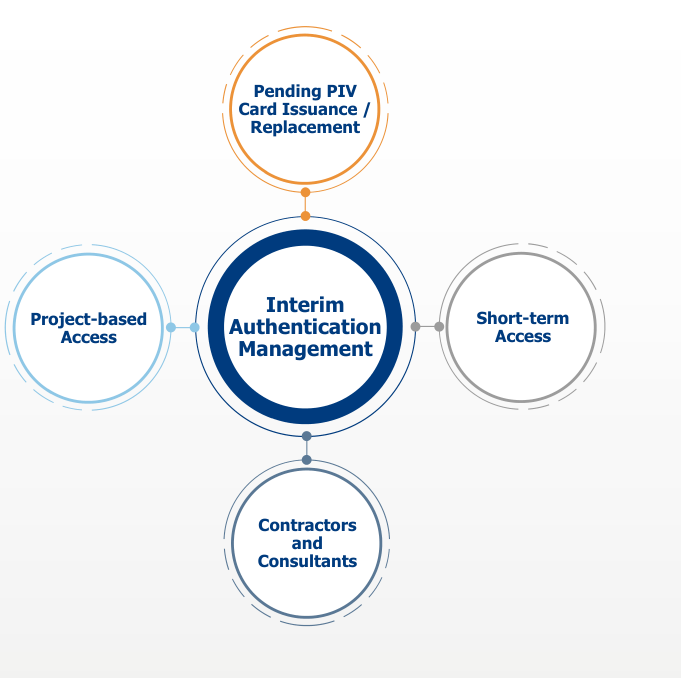
Federal Agencies must adhere to standardsfor phishing-resistant authentication. Existing systems are set up to utilizePIV cards. Yet, it can take six months to obtain a PIV card for a new employeeand weeks to replace a lost card. Many consultants are ineligible to receive aPIV card yet must be provided secure access over long timeframes. Further,employees and contractors often need short term access only for a given projector for a set timeframe. Lastly, PIV cards are not read by all devices. Forthese needs, agencies today rely on weak authentication methods. So, how caninterim authentication be made phishing resistant?
The answer is that flexible management ofauthenticators (e.g., Smart Cards and USB Keys) is needed to provide interimyet phishing-resistant authentication. This authentication must be able tohandle diverse uses such as workstation logon and short-term (with a fixed enddate) application access.
Challenges for Federal Agencies
Federal agencies require interimphishing-resistant authentication for a range of scenarios:
- Complex Environment:Multiple operating systems, workstations, Identity Providers (IdPs), and more.
- Mix of Authenticator Readers: Lacking a PIV reader, workstations may drive the use of aparticular authenticator.
- Mix of Ongoing and Temporary Access: Even long-term employees and contractors are likely to requiretemporary access for a given project.
- Multilayered Secure Access: Authentication is needed at each layer.
- Multiple Authenticators:Individuals may need to authenticate to multiple workstations at the same timeand so need multiple authenticators to be activated and maintained, each withdiscrete authentication credentials.
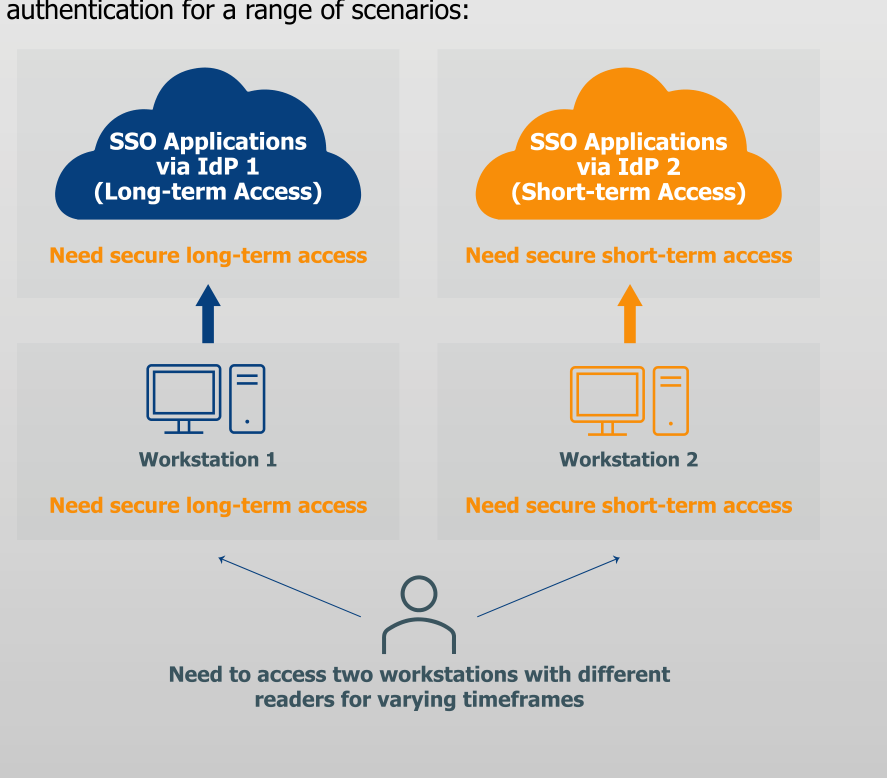
Federal Agencies need interimphishing-resistant authentication that spans all the scenarios where a PIV cardapproach isn’t feasible
Introducing Axiad Conductor
Axiad Conductor is a comprehensive,efficient, and secure authentication SaaS platform that eliminates silos acrossthe environment. Architected for best-practices security, it enables“mix-and-match” use of the Axiad Conductor product line. It can be applied inheterogeneous IT environments – e.g., organizations operating Windows, Mac, andLinux operating systems or with multiple existing IAM systems in place –allowing organizations to remove gaps and inconsistencies in how theyauthenticate across complex ecosystems, and ultimately to become moreprogrammatic in their overall cybersecurity practices.
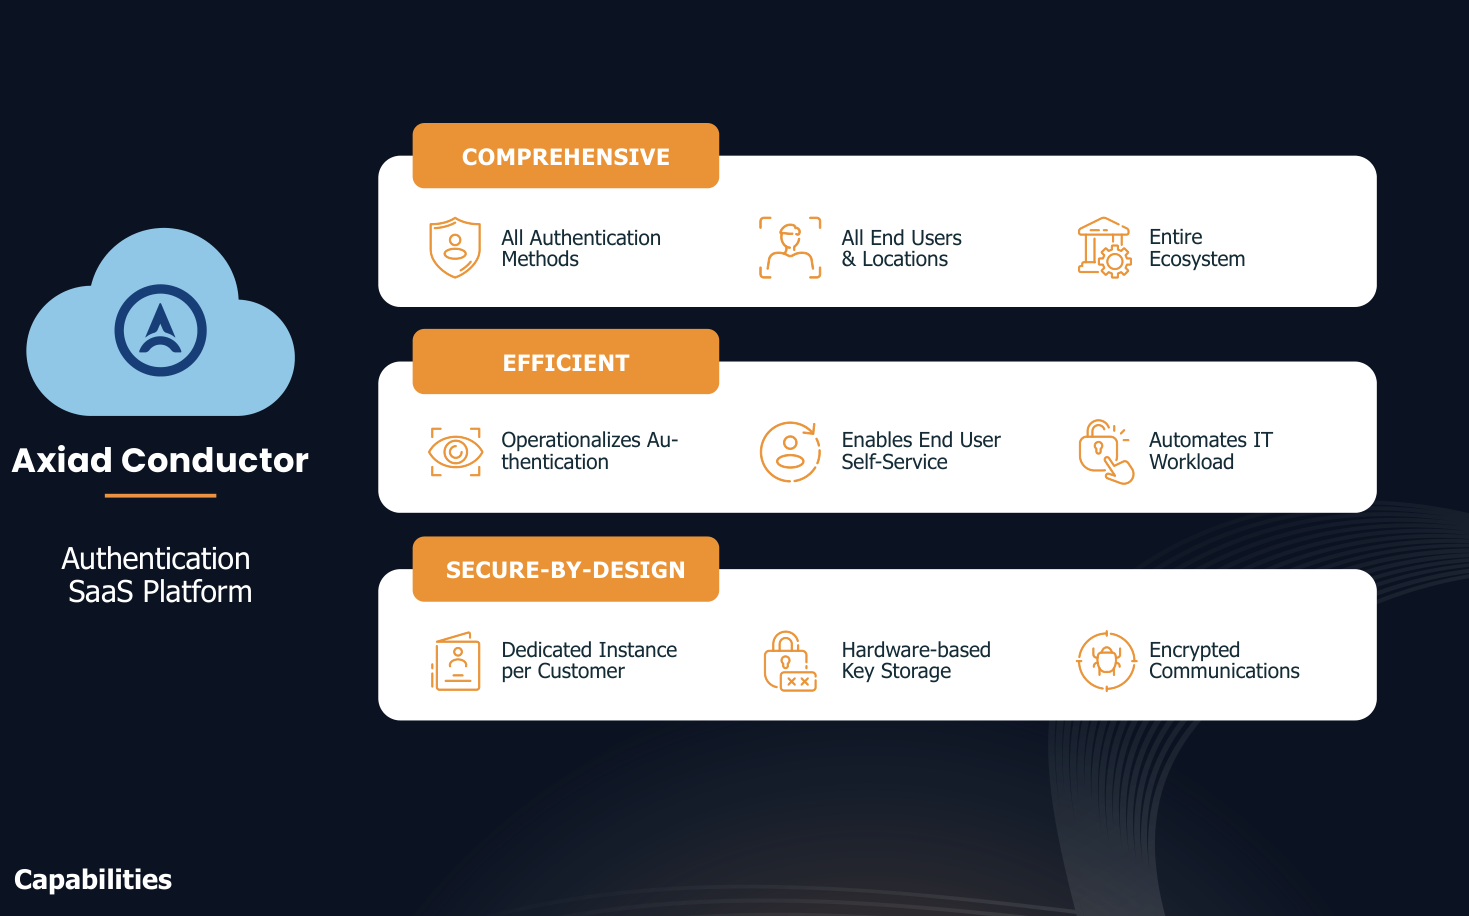
Capabilities
- Comprehensive: Supportsall authentication methods across users, machines, and more whileinteroperating with the entire Identity ecosystem
- Efficient: Streamlines andautomates help desk workload, enables end user self- service, and minimizesoverall IT overhead
- Secure-by-Design:Architecture designed with best-practices security including a private instancefor each
Interim and Non-PIV authentication management lifecycle –one example
Leveraging the Axiad Conductor platform,Axiad provides flexible and consistent Authentication Management focused on theauthenticators and credentials required for each authentication operation (suchas accessing a workstation versus an application). Key functionality:
- Broad Authenticator and Credential support: Axiad supports a broad range of phishing-resistant authenticatorsincluding PIV cards, Smart Cards, and USB Keys as well as credentials includingFIDO passkey and certificates.
- Multiple Authenticators and Credential Management: Multiple physical authenticators, each with a unique set ofcredentials, can be assigned to and managed for each end user.
- High Security Practices:To maximize security, Axiad ensures that the appropriate authenticators andcredentials are enrolled prior to workstation authentication. Further, Axiadsupports workstation authentication as a prerequisite to application access.
- Broad environment support:Authentication across Windows, Mac, and Linux, across devices, and across IAMvendors – who provide the Identity Provider (IdP) functionality – are allsupported.
- Unchanged authentication:While it leverages the appropriate authenticator and credentials, IdentityProvider (IdP) authentication processes are unchanged. As an option, Axiad canalso act as an IdP.
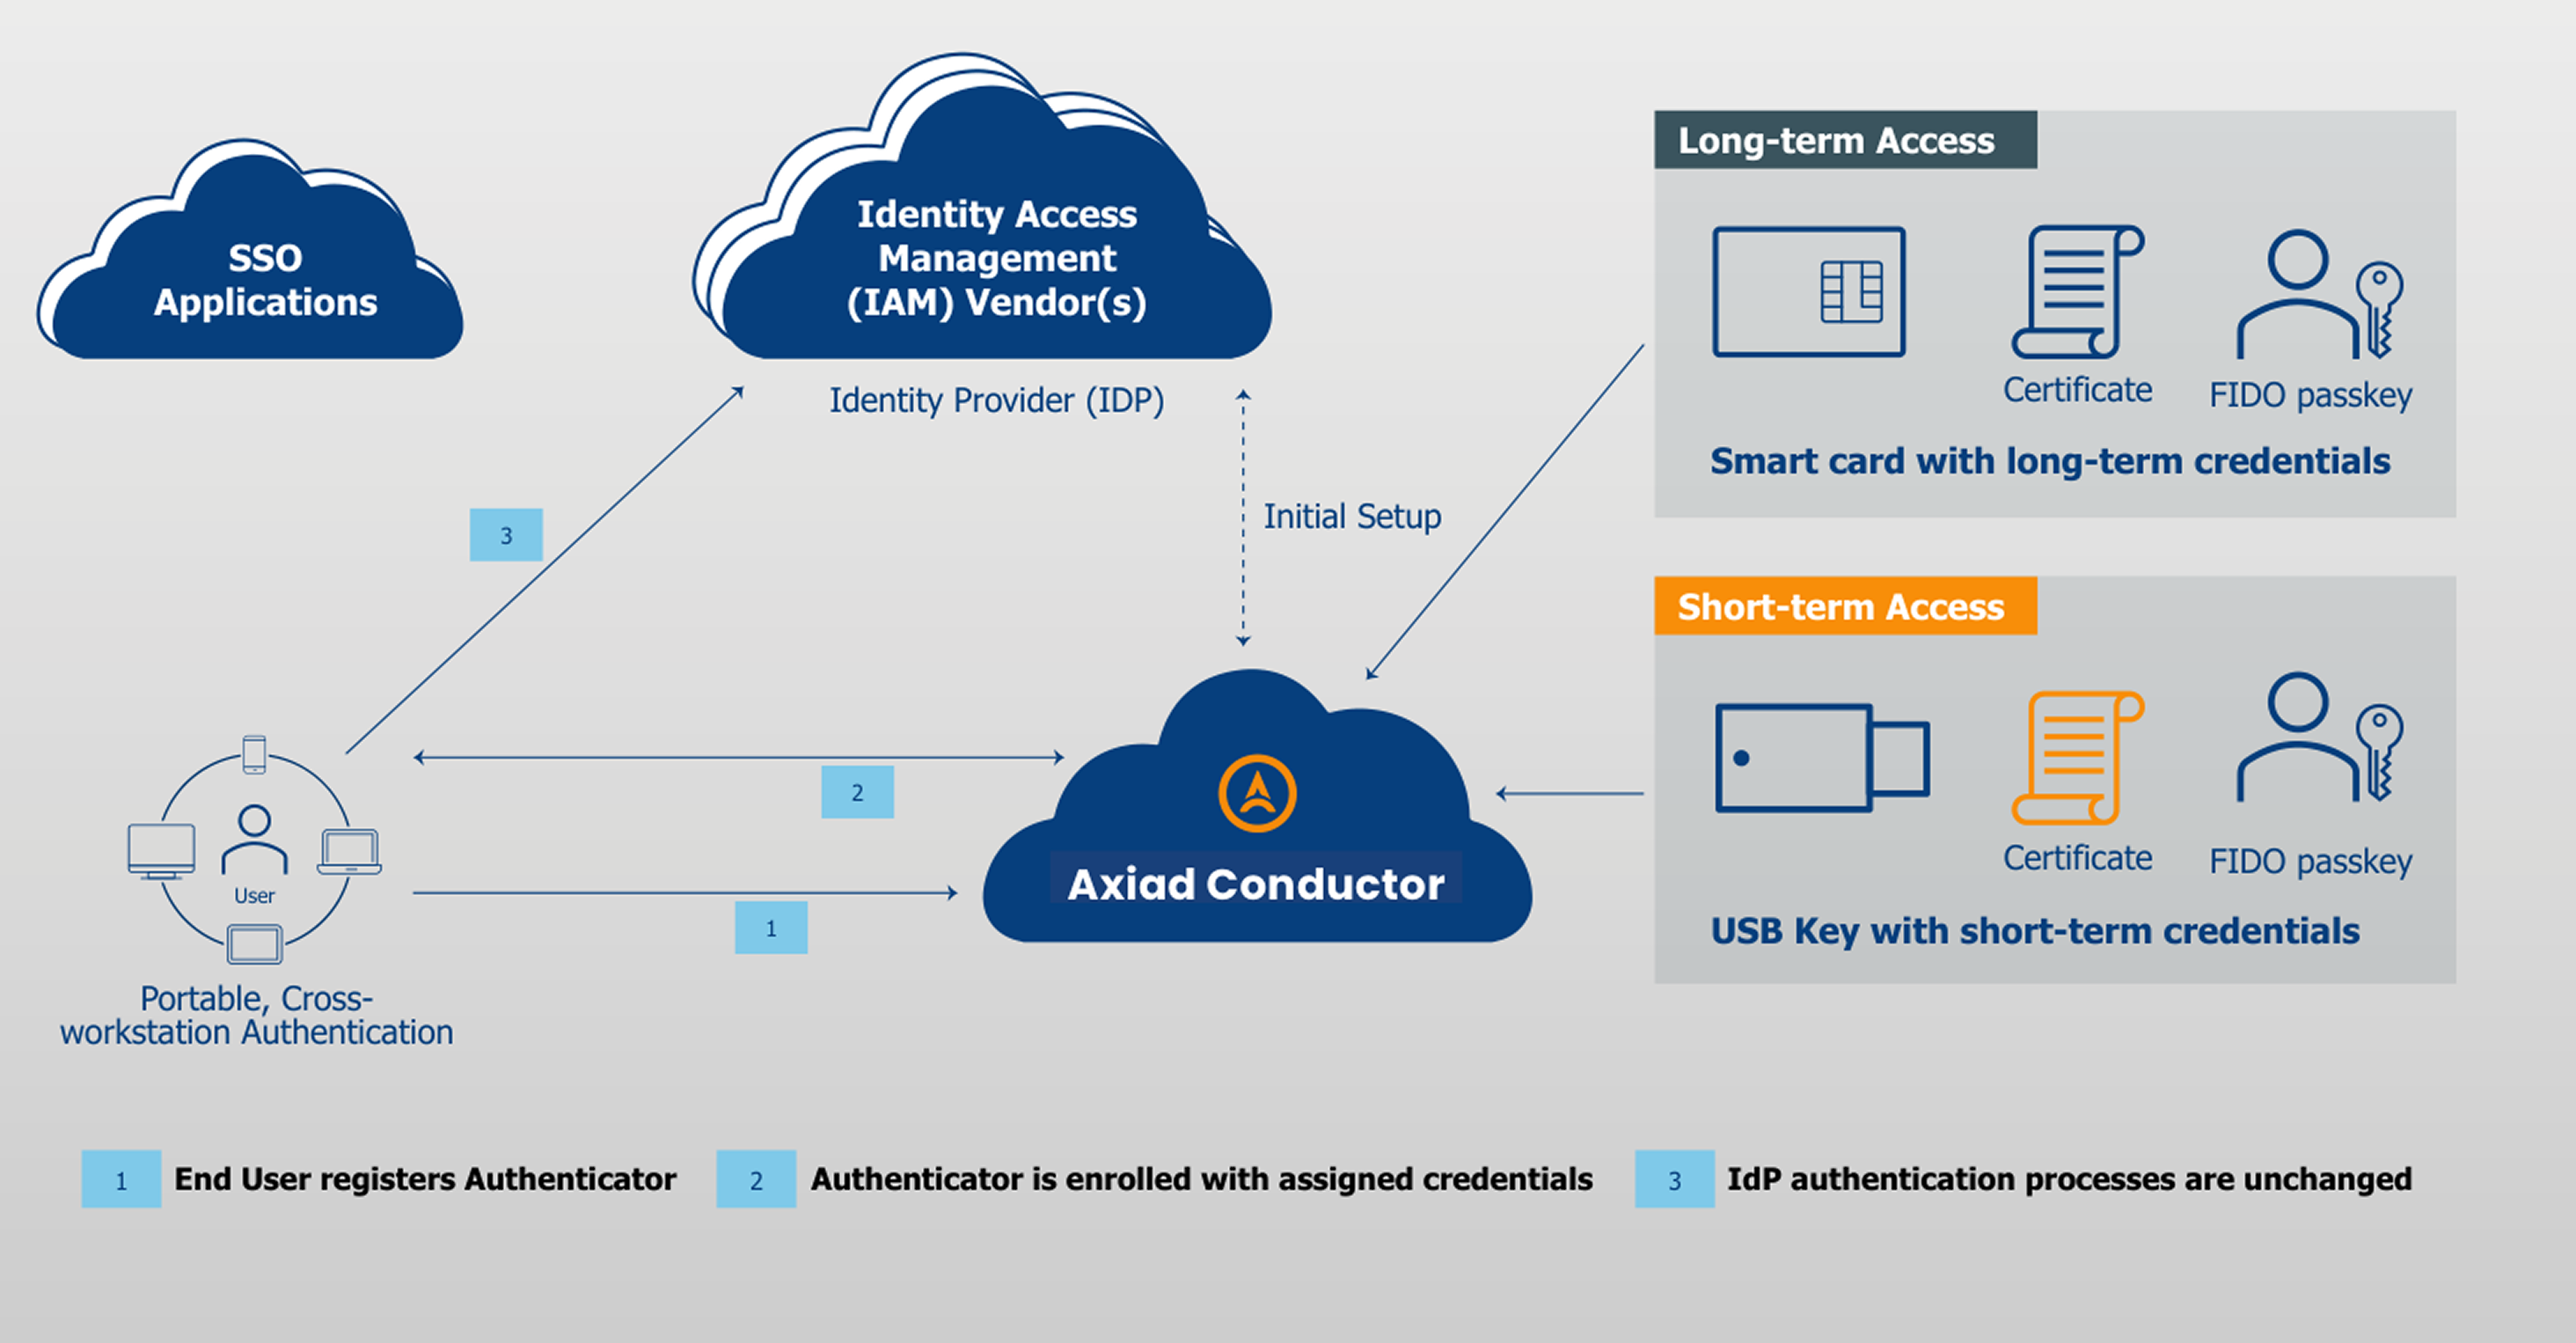
Axiad centralizes Authentication Management– including phishing-resistant authenticators and custom credentials – acrossdiverse environments including Windows, Mac, and Linux
Interim and Non-PIV authentication in use – one example
With the appropriate set of authenticators,credentials, and expiration dates defined, interim authentication is preciselycontrolled and phishing resistant to maximize security and minimize end userfriction. In this example, Smart Cards and USB Keys are chosen by the Agencydue to their ability to be read by the appropriate workstation. Keyfunctionality:
- Multilayered Secure Authentication: By supporting the issuance and maintenance of multiple credentials,each authentication process such as initial authentication to the workstationand each subsequent application access can be controlled by a customcredential.
- Custom Durations: By beingable to create customized certificates, each set of interim needs can beprecisely addressed with pre-set expiration dates.
- Choice of Authenticator Form Factors: A wide range of authenticator options enable matching to theworkstation reader.
- Mix of Ongoing and Temporary Access: By setting the expiration date of factors and whether they arerenewable or expire on a fixed date, a mix of ongoing and temporary access canbe flexibly defined for each end user and each project.
- Multiple Devices:Individuals may need to authenticate to multiple devices at the same time andso need multiple authenticators to be activated
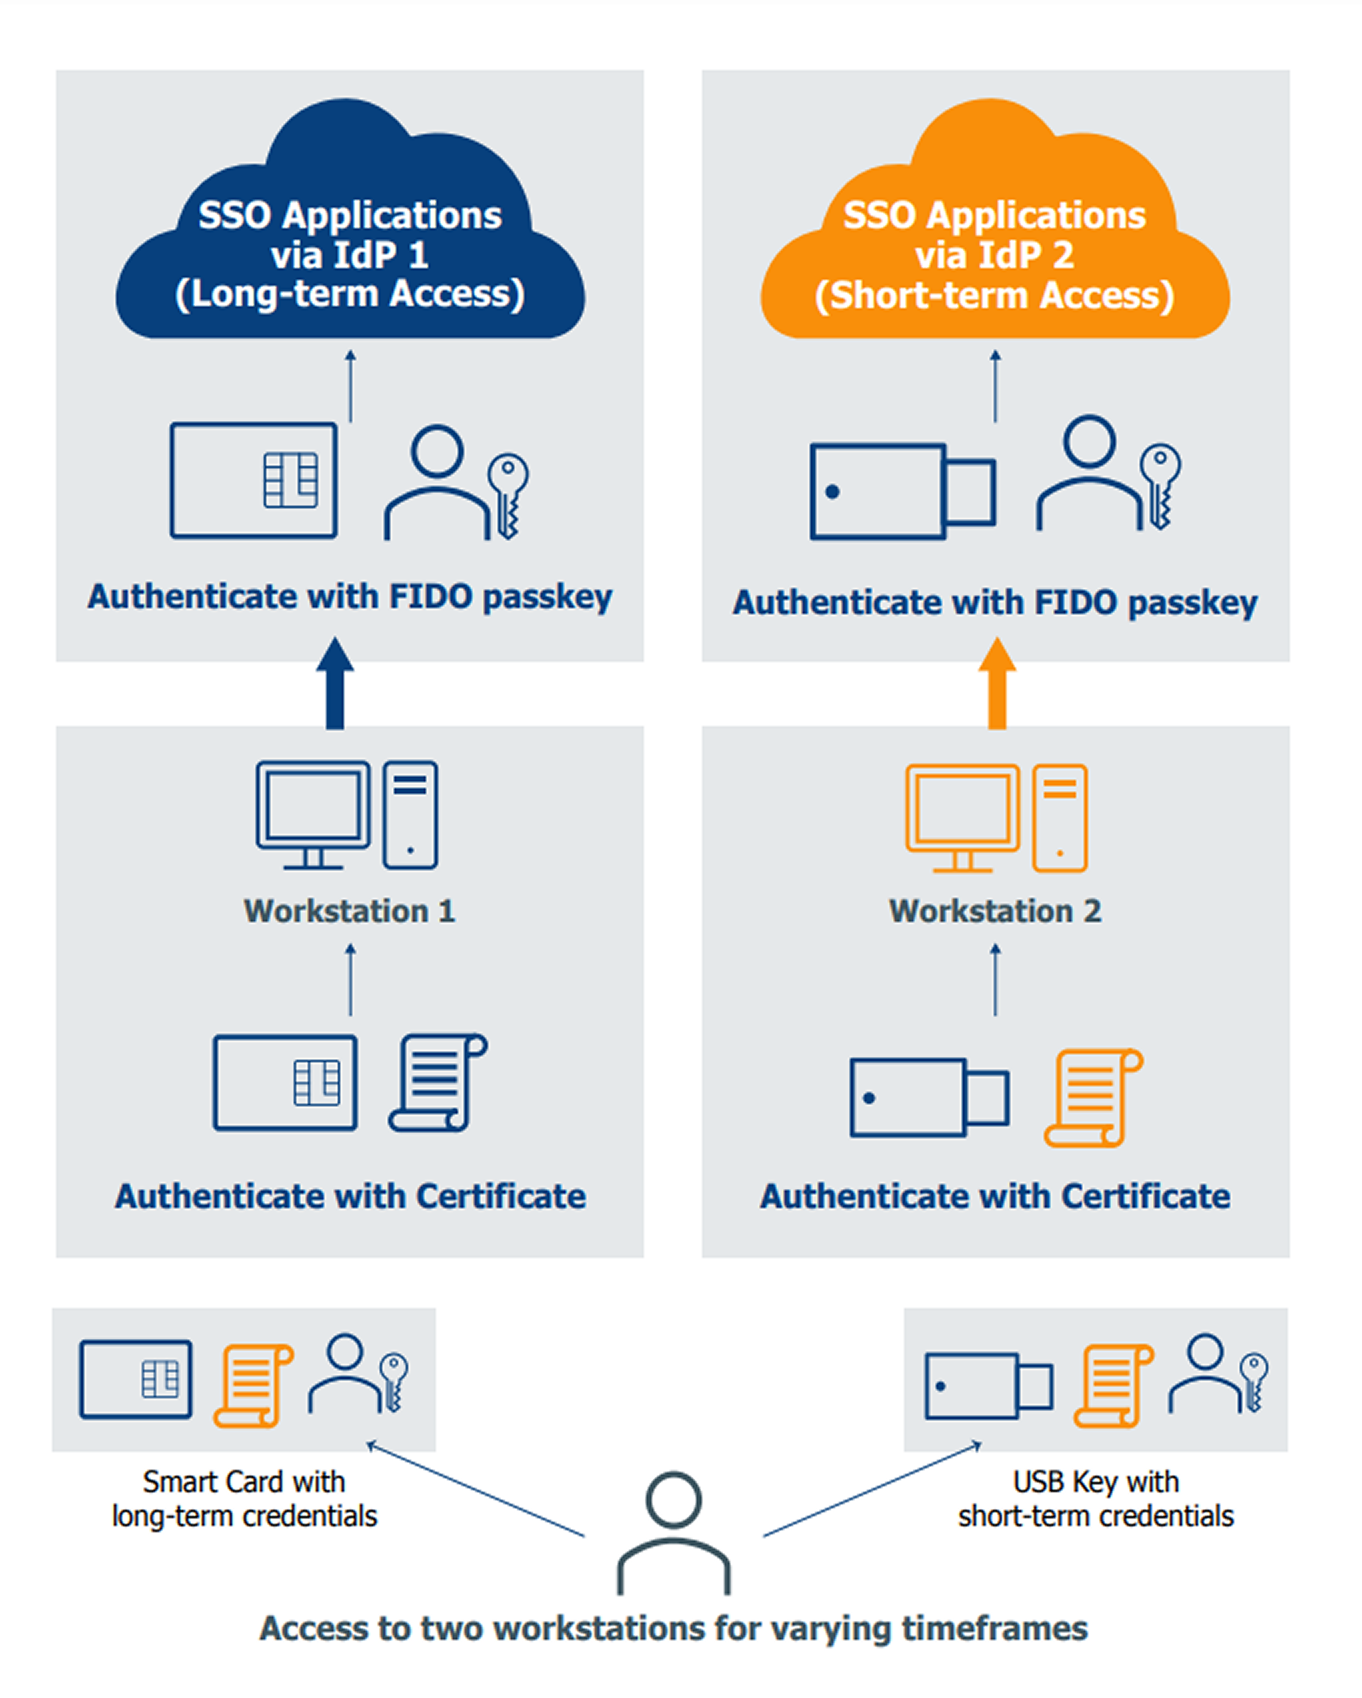
Federal Agencies can leverage centralizedAuthentication Management that provides flexible phishing-resistantauthentication for the gamut of interim needs
Unique authentication management capabilities
As of this writing, Axiad’s approachprovides capabilities that cannot be matched elsewhere:
- Consistent phishing-resistant authentication: All authentication steps can be made phishing-resistant even forinterim needs.
- Multiple device use:Multiple authenticators can be issued and efficiently manage to enable the useof multiple secured devices at the same time.
- IT efficiencies: ITefficiencies are maximized via leveraging Axiad’s utilities for authenticationlifecycle management.
Benefits for this use case
- Rock Solid Security
Government-grade phishing-resistant authentication can be enforced for each interim authentication need - Productivity Improvement
By eliminating the wait for authenticators, productivity can be improved by weeks to months - Match “Need to Know”
With precise yet flexible controls, authentication for each project can match the “need to know”
About Axiad
Axiad is an identity security company tacklingthe growing threat of compromised credentials, which drive over 70% ofenterprise breaches. The sprawl of human and non-human identities acrossorganization silos creates security blind spots that existing tools fail tosecure. Axiad tackles this problem head-on, detecting identity risks and poorcredential hygiene across systems, providing actionable insights, and enhancingsecurity without needing a complete overhaul. Axiad makes identity simple,effective, and real.


Back

Back
Back