




Authentication management at scale
Overview of use case
As many a CISO has observed, even the best security fails when end users won’t tolerate it and IT doesn’t have the cycles to make it work. Methods such as FIDO and Certificate-Based Authentication provide rigorous phishing-resistant authentication. So, what is keeping organizations from widespread adoption?
The answer is authenticators and associated credentials involve high manual effort for IT to manage. At scale, management of authenticators and credentials (“Authentication Management”) is prohibitive when factoring in issuance, account recovery, renewal, and revocation efforts: across the lifecycle. Existing identity products, while providing authentication for end users, do not provide these capabilities.
Challenges at scale
Authentication Management challenges are significant and can break the organization’s back at scale.
- End User Experience: Today, organizations are pinned between the high friction of legacy authentication (passwords) and legacy MFA (push notifications) versus the difficulties in provisioning phishing-resistant authentication. This friction often leads to end users circumventing authentication security or resisting new methods of authentication. So, end user experience must be addressed:
- Security Levels: Security must be tailored to the security requirements and needs of each end user group.
- Provisioning: Provisioning for end users must be convenient and efficient.
- Key needs such as account recovery and renewals must be self-service rather than subject to help desk delays.
- Self-Service: Key needs such as account recovery and renewals must be self-service rather than subject to help desk delays.
- IT Oversight: Due to authentication siloes by Operating System, IAM, etc., IT is not able to visualize the state of authentication management. To do so, IT needs new capabilities:
- Unification: Authentication siloes must be bridged by a unified approach.
- Visibility: The overall state of the authenticator and credential rollout and current status must be visible.
- Lifecycle Management: IT must be able to manage authenticators and credentials as a lifecyle that can efficiently handle provisioning and renewals at scale.
- IT Resource Limits: A recent whitepaper calculates that each end user authentication provisioning request takes approximately 30 minutes to complete.1 At scale, IT teams simply do not have the resources to manage multiple, complex, and unique authentication systems manually. IT needs a unified approach with builtin efficiencies to roll out and manage phishingresistant authentication.
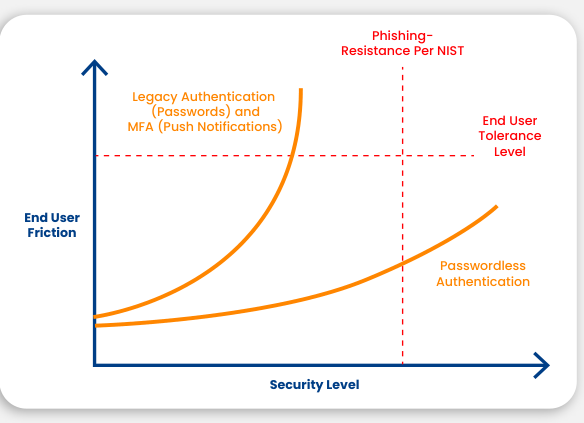
Summingup, clearly IT cannot survive without systematic Authentication Management,including end user self-service where it does not compromise overall security.
Introducing Axiad Conductor
Overview
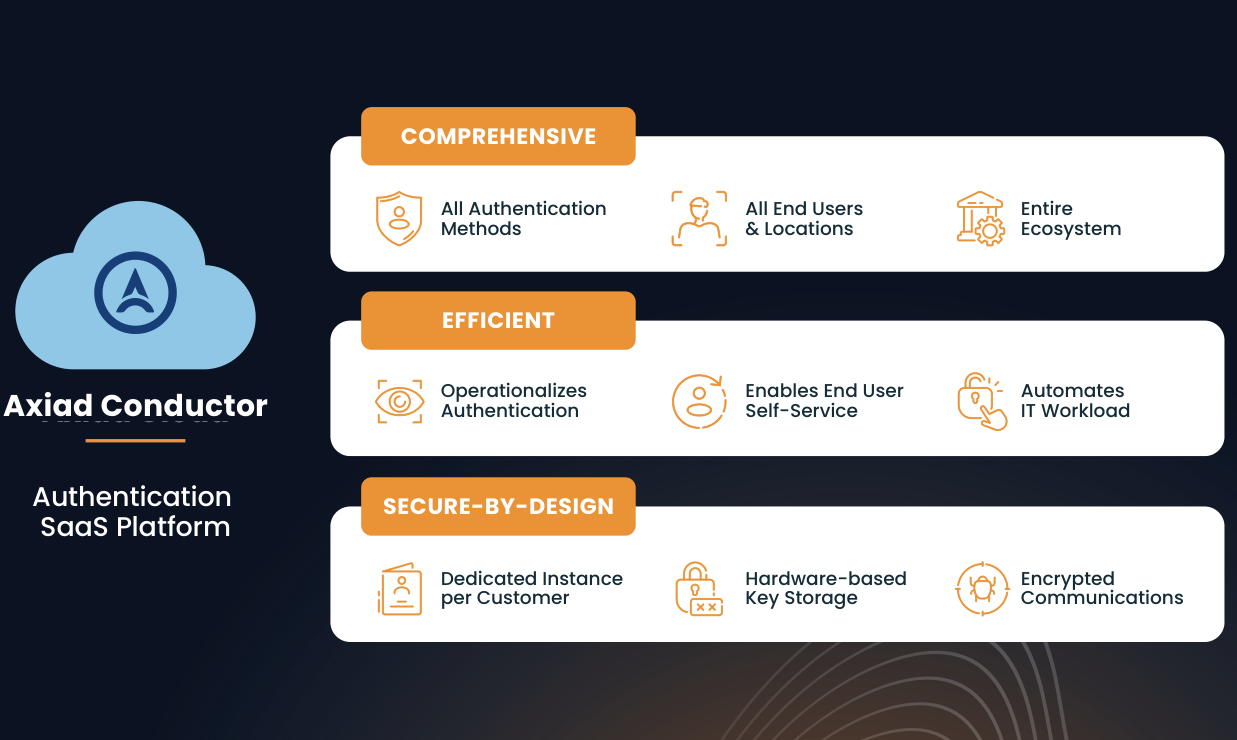
Axiad Conductor is a comprehensive,efficient, and secure authentication SaaS platform that eliminates silos acrossthe environment. Architected for best-practices security, it enables “mix-andmatch”use of the Axiad Conductor product line. It can be applied in heterogeneous ITenvironments – e.g., organizations operating Windows, Mac, and Linux operatingsystems or with multiple existing IAM systems in place – allowing organizationsto remove gaps and inconsistencies in how they authenticate across complexecosystems, and ultimately to become more programmatic in their overallcybersecurity practices.
Capabilities
- Comprehensive:Supports all authentication methods across users, machines, and more while interoperating with the entire Identityecosystem
- Efficient:Streamlines and automates help desk workload, enables end user self- service,and minimizes overall IT overhead
- Secure-by-Design:Architecture designed with best-practices security including a private instance for each customer, key storage inspecialized hardware, and encrypted communications.
How Axiad helps you
Overview
Axiad’s SaaS Conductor Platformoperationalizes an AuthenticationManagement Lifecycle at scale:
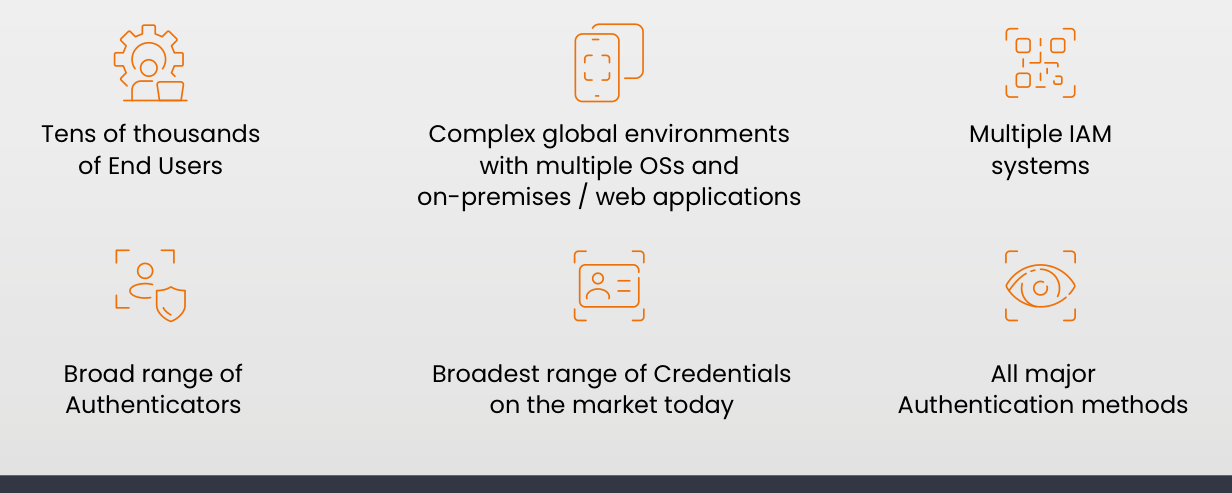
TO ACCOMPLISH THIS MISSION, AXIAD PROVIDES AUTHENTICATIONMANAGEMENT LIFECYCLE FOR BOTH IT AND END USERS:
- ITcapabilities:
- Define the authenticator options and corresponding credentials
- Optimize the Rollout of MFA across the organization
- Manage any incidents
- Renew with new or reset credentials
- End Usercapabilities:
- Enroll the authenticator(s) of choice
- Issue credentials onto theauthenticator
- Recover colleagues’ accounts without IT intervention
- Renew credentials either for account recovery or at expiration
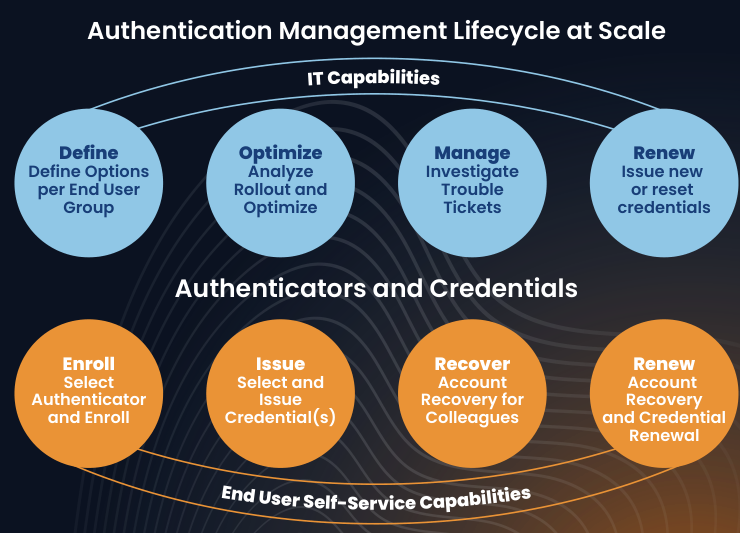
Thelifecycle can be broken down by main processes:
- Provisioning by IT and End Users
- Authentication Management Lifecycle — IT
- Authentication Management Lifecycle —End Users.
1. Provisioning by IT and End Users
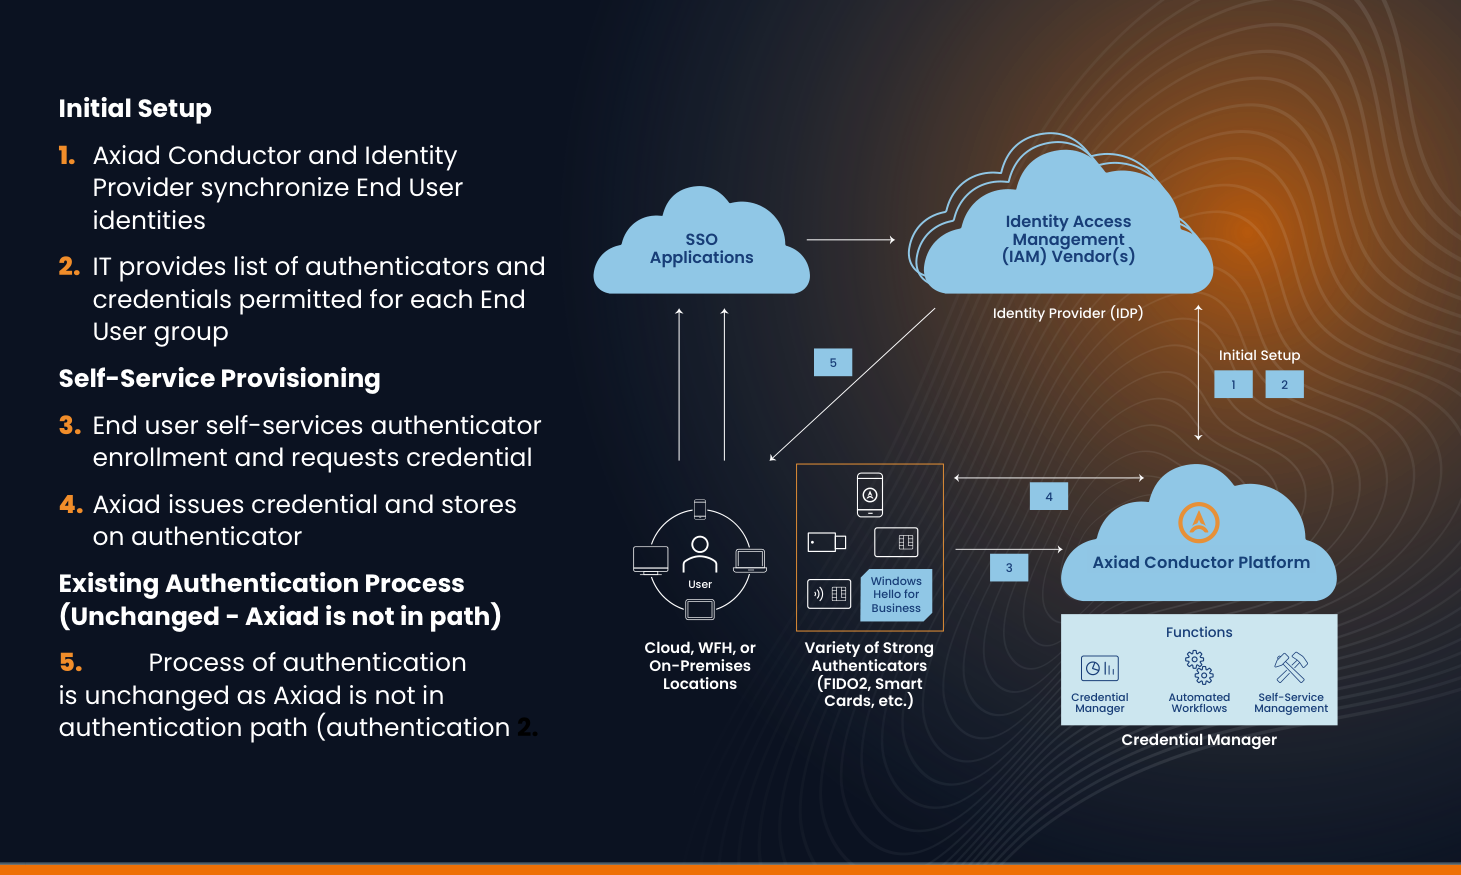
Once IT defines the authenticators andcredentials by end user group, provisioning tasks (enrollment of authenticatorand issuance of credentials) are self-service.
Define
IT sets up the list of authenticators (suchas YubiKeys, Smart Cards, Windows Hello for Business, Axiad ID mobileauthenticator, and more) that are allowed for the organization overall and foreach group of users as needed. IT also specifies the credentials that areallowed such as X.509 Certificates, OTP, FIDO2, and more.
Enroll
Once setup is done, all provisioningoperations can be self-service by end users. Where allowed by IT, the end usercan select the authenticator from the pool and enroll it with Axiad.
Issue
When the credential is requested, it isthen automatically issued and stored on the selected authenticator.
Recover
When Account Recovery is needed, Axiadenables self-service based on user groups. Leveraging policies defined by theIT team, colleagues within a defined “circle of trust” are authorized to reseteach others’ credentials. Productivity savings include time spent on the phonewith Help Desk, Help Desk’s time, and of course delays when outside of normalworking hours.
Renew
Credentials must be periodically renewedper the organization’s and/or the service provider’s policies. Axiad promptsthe End User to renew or revoke the credential without needing IT intervention.As a result, end users more efficiently manage their credentials and sominimize disruptions due to expired credentials.
3. Authentication Management Lifecycle by IT
Optimize
Because of consolidating authenticator andcredential management into a single platform, IT gets actionable visibilityinto the rollout of authenticators and credentials. Axiad tabulates end usersby authentication method such as UserID / Password, Legacy MFA (PushNotifications), and MFA (CBA, FIDO2, and more). As a result, IT can efficientlyroll out authentication to groups of end users. Optimization, such as decidingwhich groups of end users should leverage strong authenticators such asYubiKeys and Smart Cards, can then be performed by IT. Status of the rollout istracked so that IT can view progress and adjust as needed.
Manage
When End Users report issues that theycannot resolve via self-service, Axiad’s Unified Portal enables IT toinvestigate the issue and take the appropriate action such as issue a newauthenticator, reset a credential, or report the issue for furtherinvestigation.
Renew
Just as for initial rollouts, Axiadutilities enable IT to roll out new credentials or to renew existing across theend user base.
Organizational outcomes
Strong positive outcomes are driven byAxiad’s approach:
- Increasedapplication deployment speed: Today, authenticationmust be designed, deployed, and testedfor each custom and vendor application and across the environment. With a unified authentication management approach, anew application just needs to specify theauthentication needed and risks and bottlenecks are addressed as part ofongoing Authentication Managementoperations.
- Match Security Spendto Business Need: An outcome of authenticationoptimization is that the security leveland corresponding spend can be matched to the business need. Instead of a one- size-fits-allauthentication approach, each business group gets the security that they need.
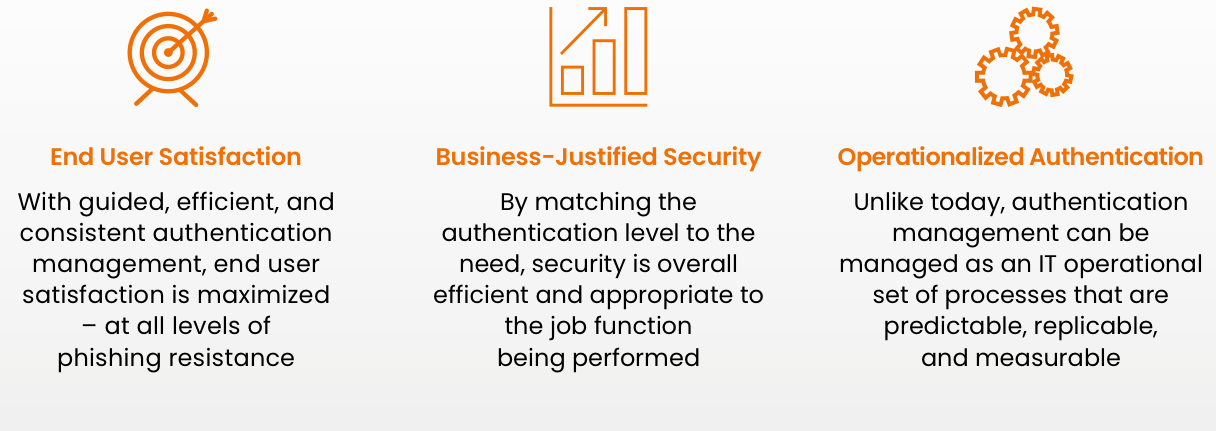
- Improve EndUser Satisfaction: Passwordless authentication,despite embodying a more rigorous levelof security, is much easier to execute for end users. As a result, end usersatisfaction will increase – a win-winfor IT!
- Increase EndUser Efficiencies: Eliminating the time that endusers spend on password lookup and on holdwith Help Desk measurably increases the efficiency of all end users – includingthe exec team. A key metric from asecurity behavior report indicates that end users spend over 12 minutes perweek just finding and resettingpasswords – with a total cost per organization of over $5.2 million per year.2
- Maximize IT /Help Desk Leverage: Axiad transforms authenticationmanagement into an ongoing activity thatcan be optimized, can be scheduled for major items such as implementing a new authenticator, and can be made radically moreefficient as compared to today’s ad-hoc approaches.
Unique authentication management capabilities
As of this writing, Axiad’s approach providescapabilities that cannot be matched elsewhere:
- Authentication Can Be Operationalized: Operations teams can treat authentication management as any otheroperational process and lifecycle.
- Actionable Visibility: The state of authentication rolloutsacross the environment is visible and actions that can shape the rollout areknown.
- Predictable events and intervals: Authentication management istreated as a lifecycle with known events (renewals and revocations) at givenintervals for action (such as at credential renewal or at end of lifecycle).
- Securityoptimized to business need: Security level andcorresponding costs can be matched tobusiness need.
- Robust Authentication Options: The broadest range ofauthentication methods, authenticators, and credentials across the broadestenvironment are managed by a single platform, eliminating siloes and reducingthe chances of a breach.
- End User Control / Satisfaction: End User control is maximized bylow-friction processes and control over credentials for themselves and forco-workers.
- LifecycleEfficiencies: Every step of the lifecycle is mademore efficient for both IT and End Users.
- IT efficiencies: Maximized since formerly one-off manualprocesses are instead offloaded via selfservice or automated via purpose-builtutilities.
- End User efficiencies: Features are optimized for end userconvenience and overall security.
Benefits for this use case
About Axiad
Axiad is an identity security companytackling the growing threat of compromised credentials, which drive over 70% of enterprise breaches. Thesprawl of human and non-human identities across organization silos createssecurity blind spots that existing tools fail to secure. Axiad tackles thisproblem head-on, detecting identity risks and poor credential hygiene acrosssystems, providing actionable insights, and enhancing security without needinga complete overhaul. Axiad makes identity simple, effective, and real. Discovermore at axiad.com or follow us on LinkedIn.


Back

Back
Back